Snowflake 管理、治理與協作
Emily Melhuish
Technical Curriculum Developer, Snowflake


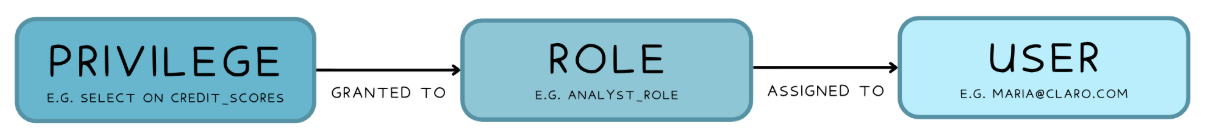
權限是執行動作的准許:
SELECT:讀取INSERT:寫入CREATE:建立| Term | Definition |
|---|---|
| Privilege | Permission to perform an action (e.g. SELECT, INSERT, CREATE) |
| Object | Anything a privilege can be granted on (table, schema, database, warehouse) |
| Role | An entity to which privileges are granted; can be granted to users or other roles |
| User | A person or service account that connects to Snowflake and holds roles |

將權限授與角色
GRANT SELECT ON TABLE core.credit_scores
TO ROLE analyst_role;
將角色指派給使用者
GRANT ROLE analyst_role TO USER maria;

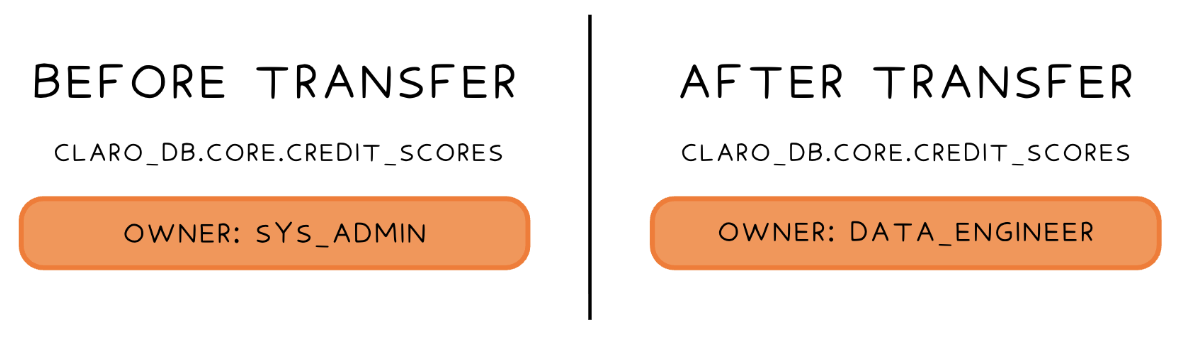
將擁有權轉移給其他角色
-- 目前擁有者:SYSADMIN
GRANT OWNERSHIP ON TABLE core.credit_scores
TO ROLE data_engineer
REVOKE CURRENT GRANTS;

GRANT USAGE ON DATABASE <your_database>
TO ROLE analyst_role;
GRANT USAGE ON SCHEMA core
TO ROLE analyst_role;
GRANT SELECT ON TABLE core.credit_scores
TO ROLE analyst_role;
| Role | Responsibility |
|---|---|
| ACCOUNTADMIN | Full account control |
| SYSADMIN | Creates databases and warehouses |
| SECURITYADMIN | Network policies, masking policies, role management |
| USERADMIN | Creates users and assigns roles |
| PUBLIC | Default role for every user |
Snowflake 管理、治理與協作