Geliştiriciler için AWS Güvenliğini Kullanma
Rahul Singh
Technical Product Manager
{
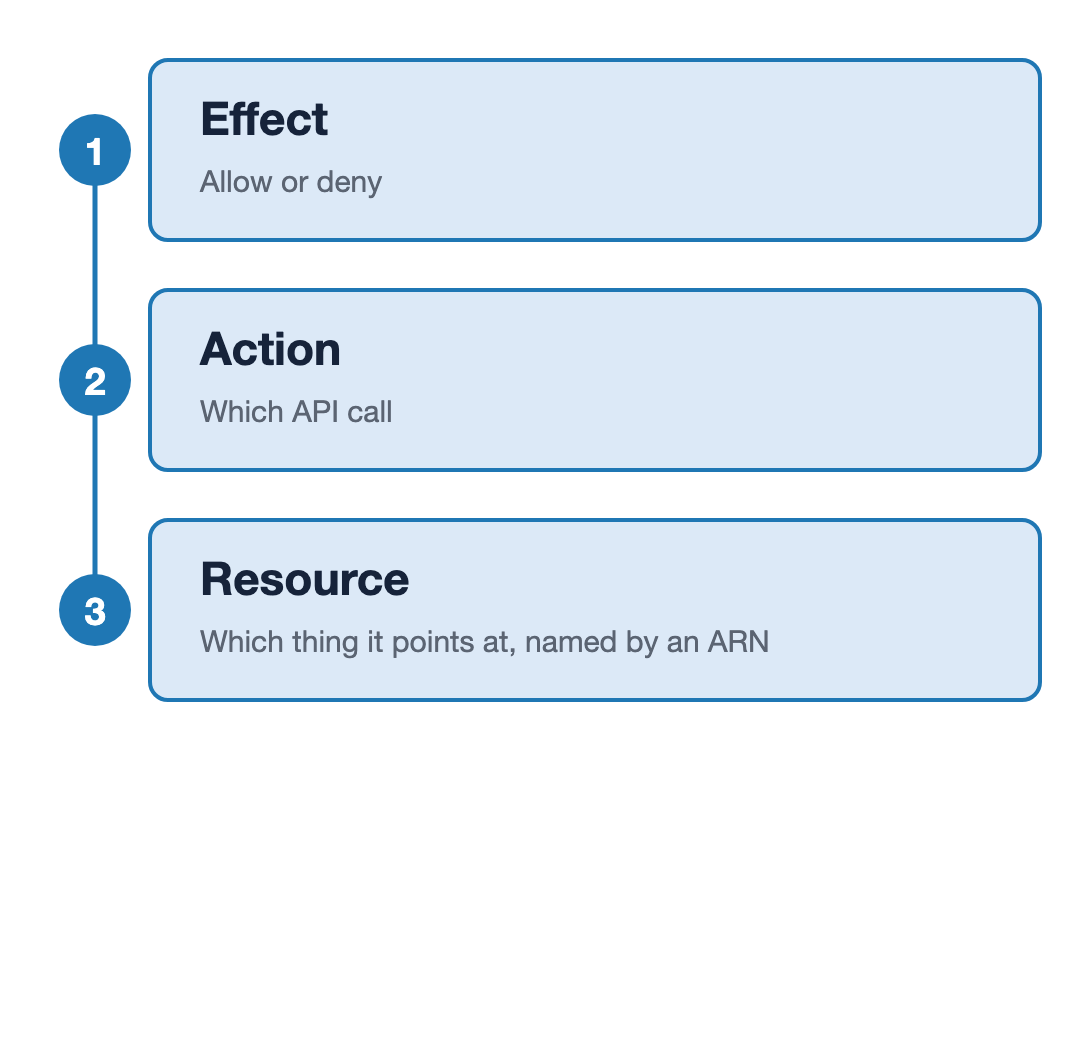
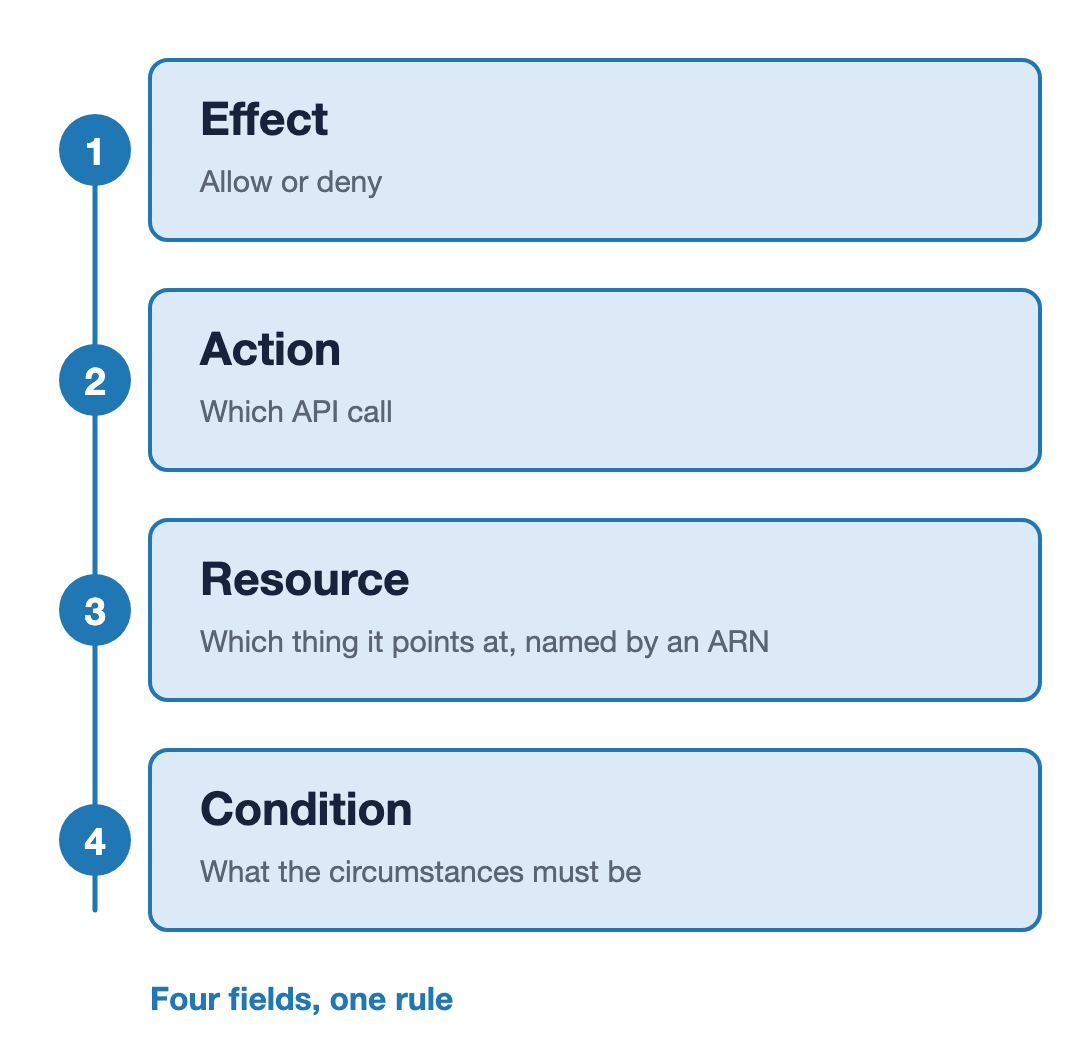
"Effect": "Allow",
"Action": "s3:GetObject",
"Resource": "arn:aws:s3:::reports/*",
"Condition": {
"Bool": {
"aws:SecureTransport": "true"
},
"IpAddress": {
"aws:SourceIp": "203.0.113.0/24"
}
}
}

{
"Effect": "Allow",
"Action": "s3:GetObject",
"Resource": "arn:aws:s3:::reports/*",
"Condition": {
"Bool": {
"aws:SecureTransport": "true"
},
"IpAddress": {
"aws:SourceIp": "203.0.113.0/24"
}
}
}

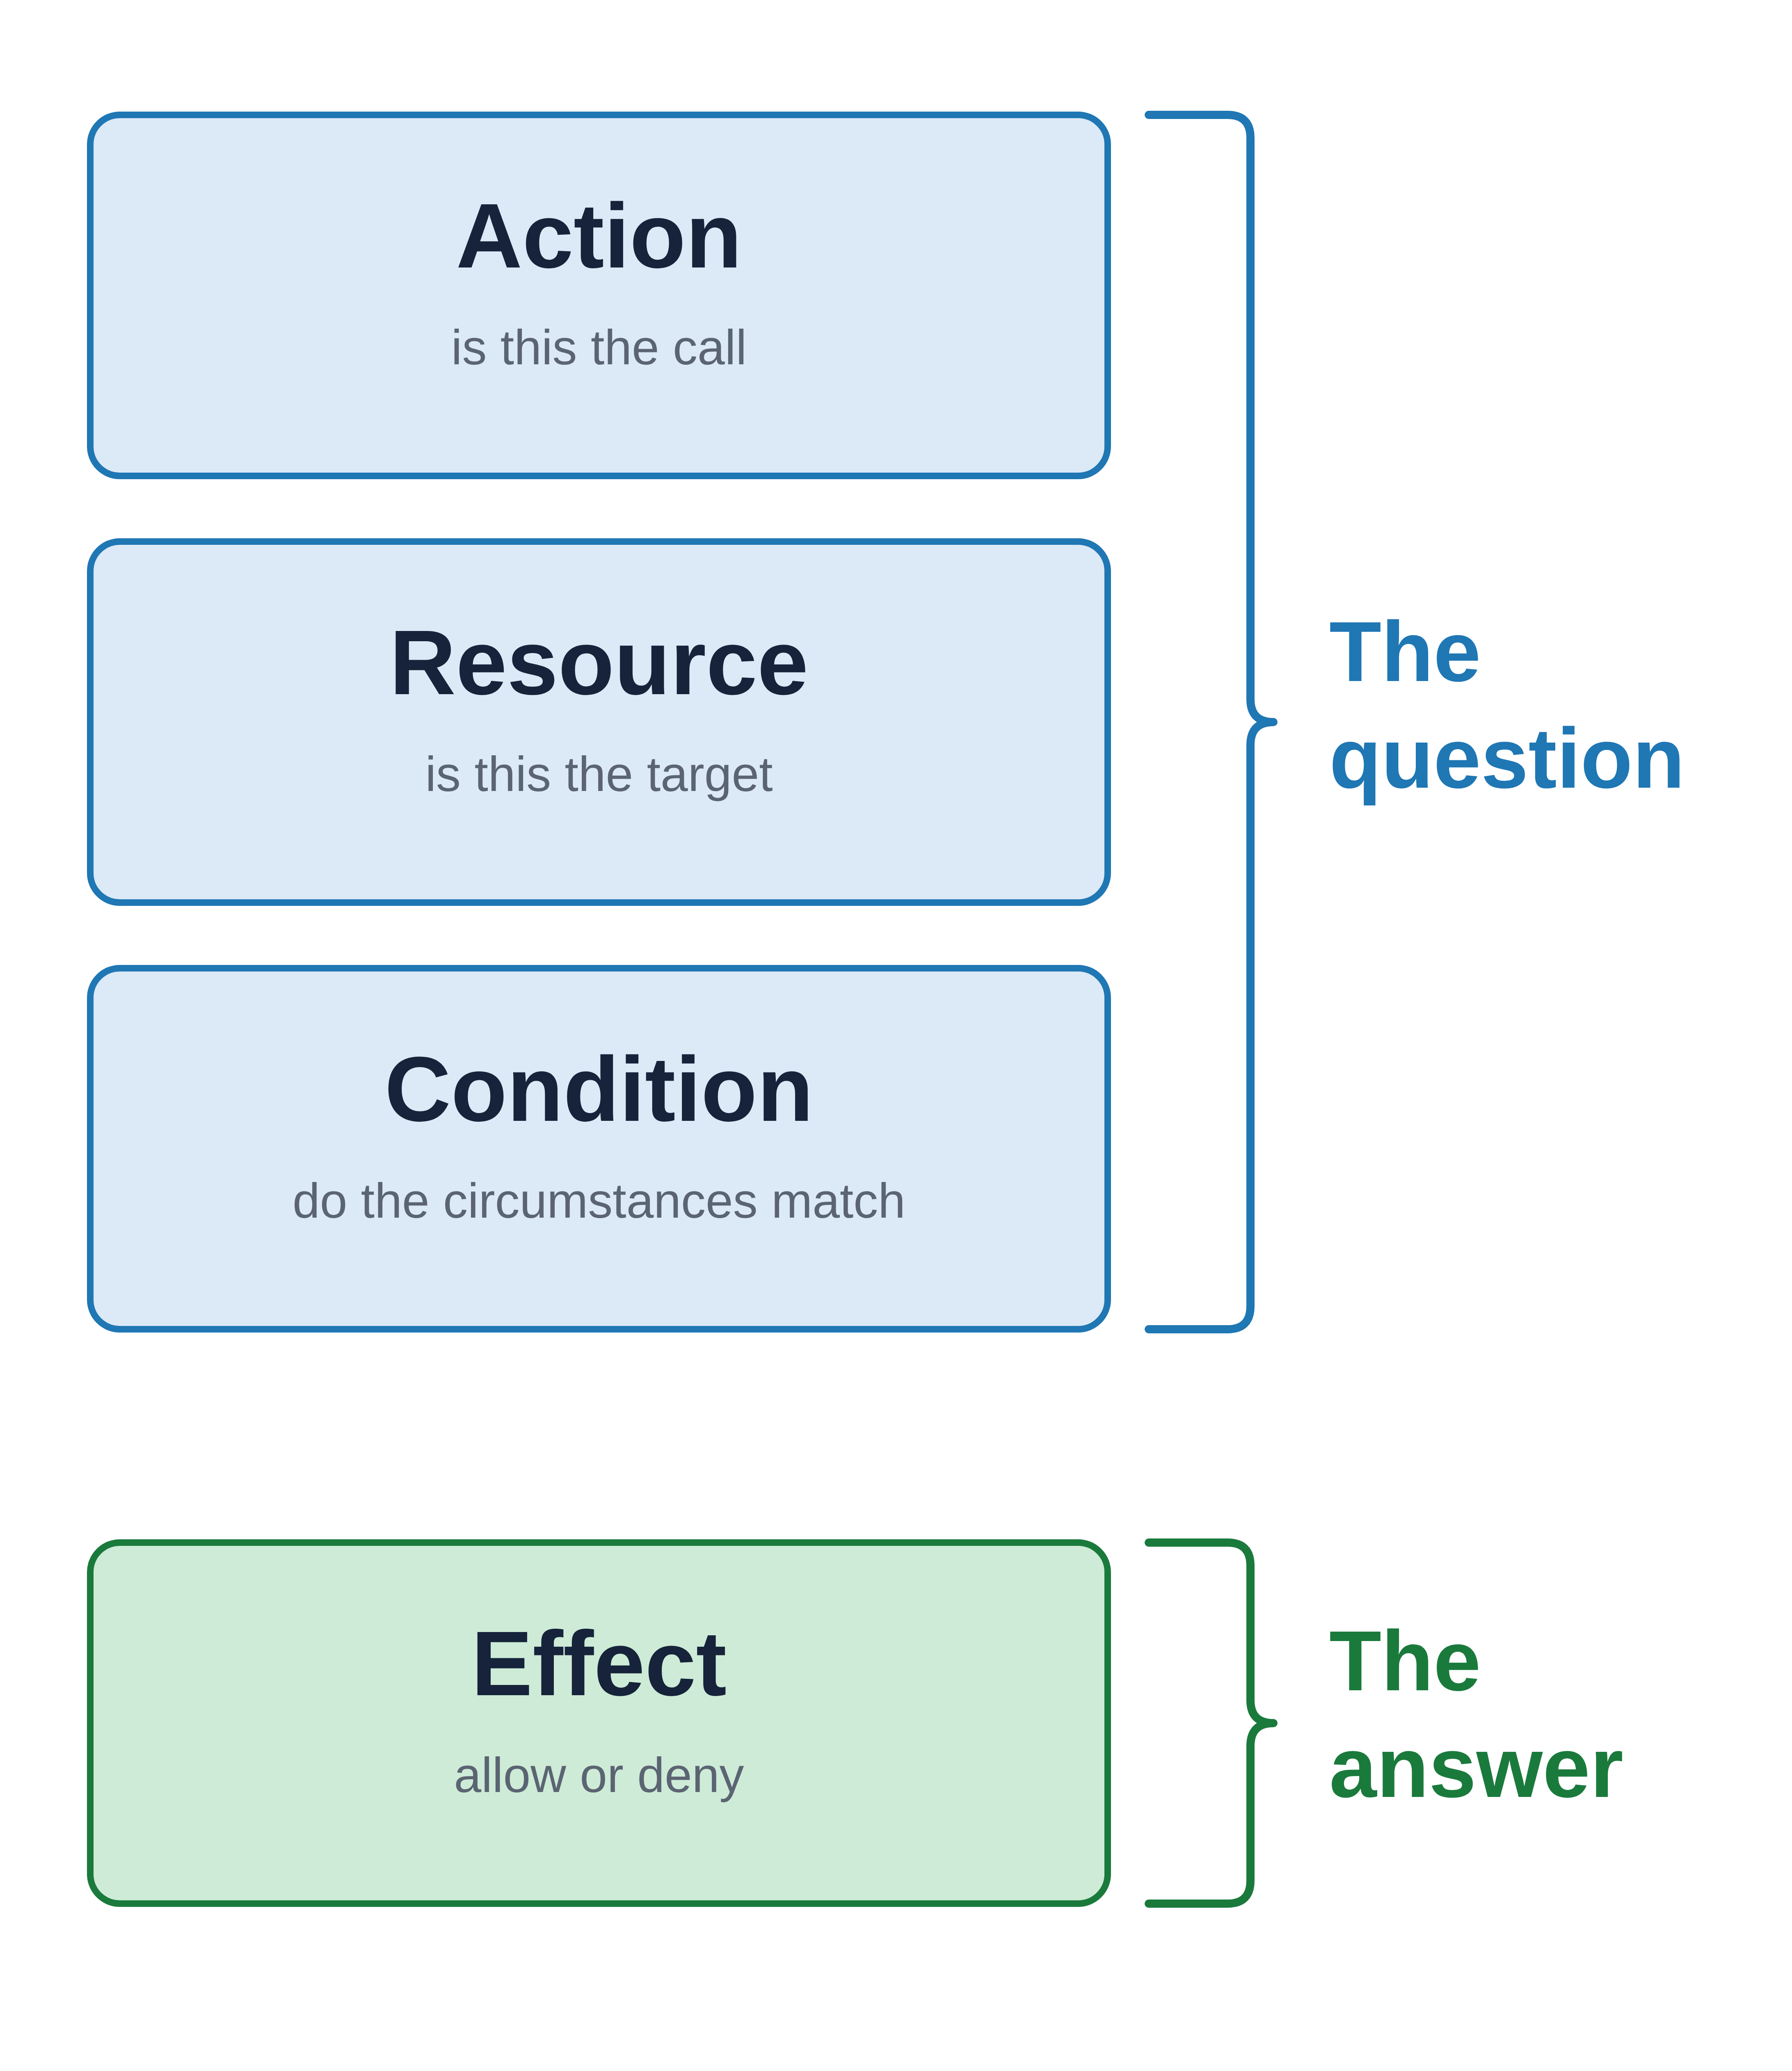
Soru
Yanıt


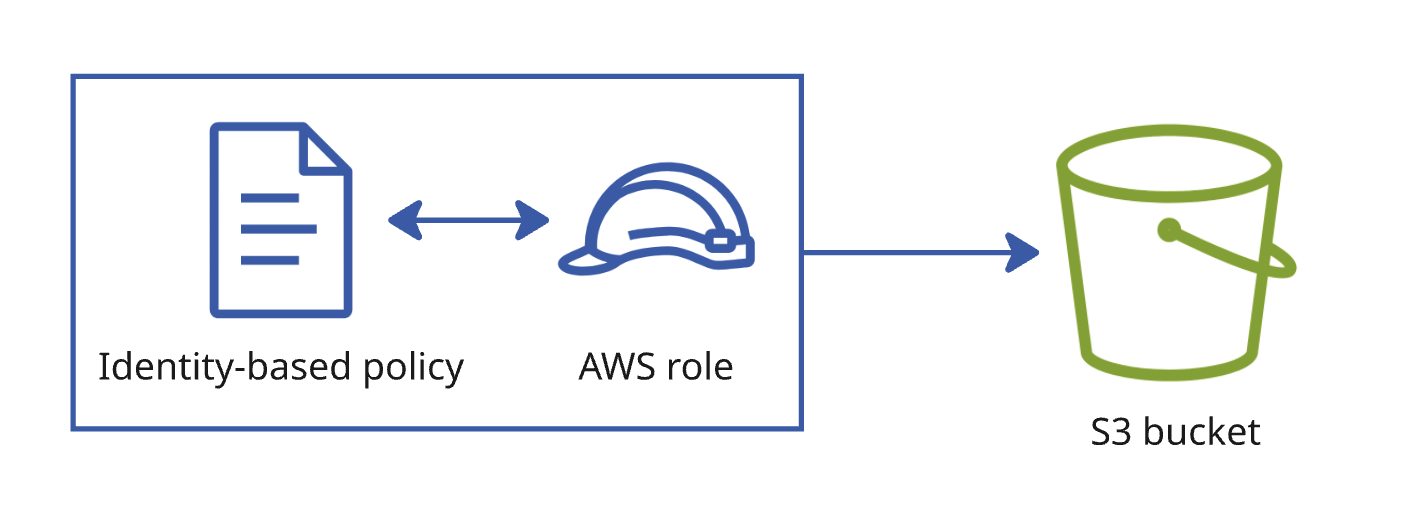
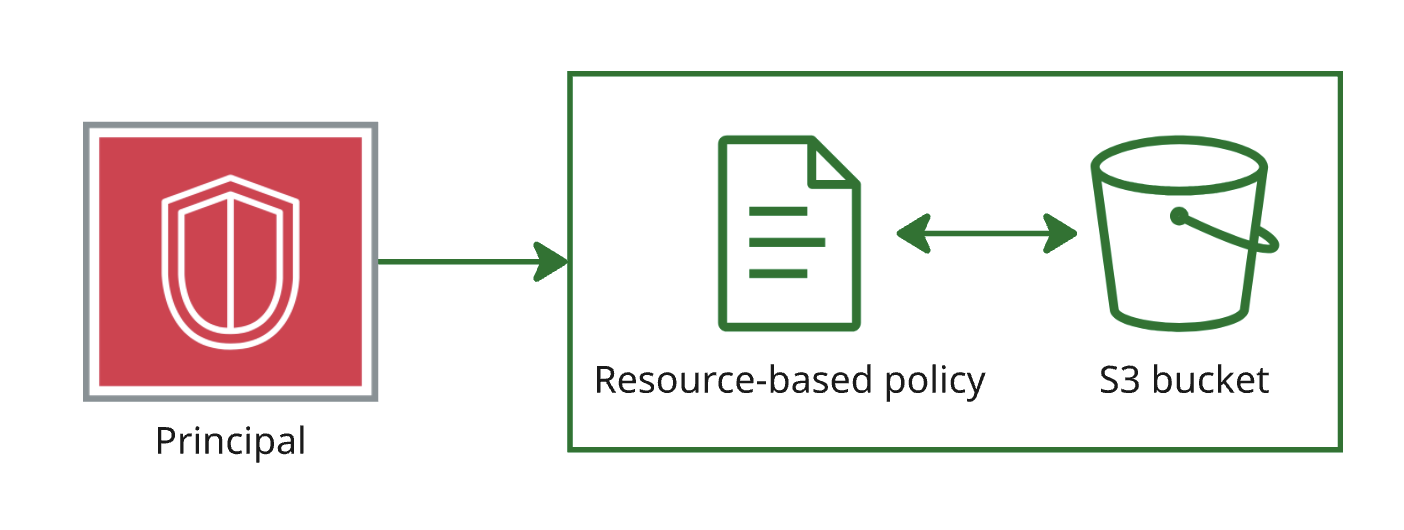
Kimliğe dayalı


Kimliğe dayalı
Kaynağa dayalı
{"Effect": "Allow", "Action": "s3:*", "Resource": "*"}
{"Effect": "Deny", "Action": "s3:DeleteObject", "Resource": "*"}
{"Effect": "Allow", "Action": "s3:*", "Resource": "*"}
{"Effect": "Deny", "Action": "s3:DeleteObject", "Resource": "*"}
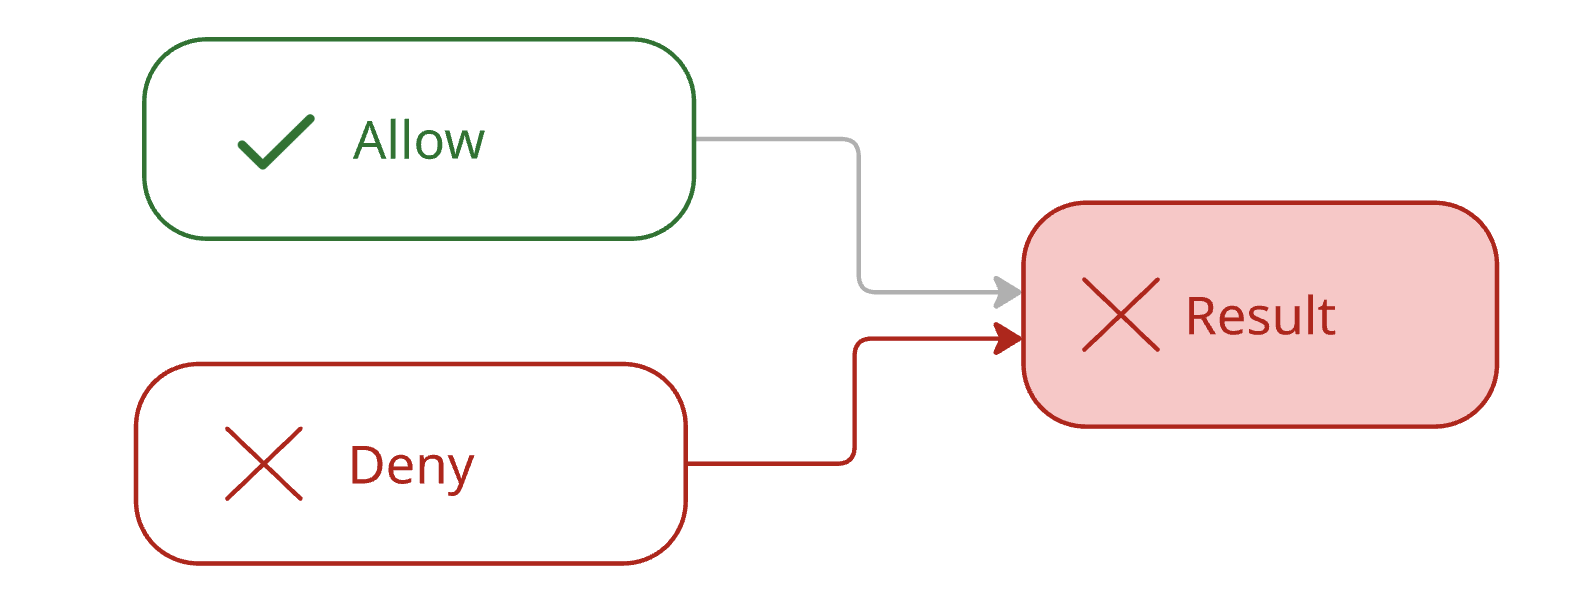
İstek: s3:DeleteObject sonucu: Reddedildi.
Açık bir deny, ne kadar geniş olursa olsun her allow'u yener


{"Effect": "Allow", "Action": "s3:*",
"Resource": "*"}
{"Effect": "Deny", "Action": "s3:DeleteObject",
"Resource": "*"}
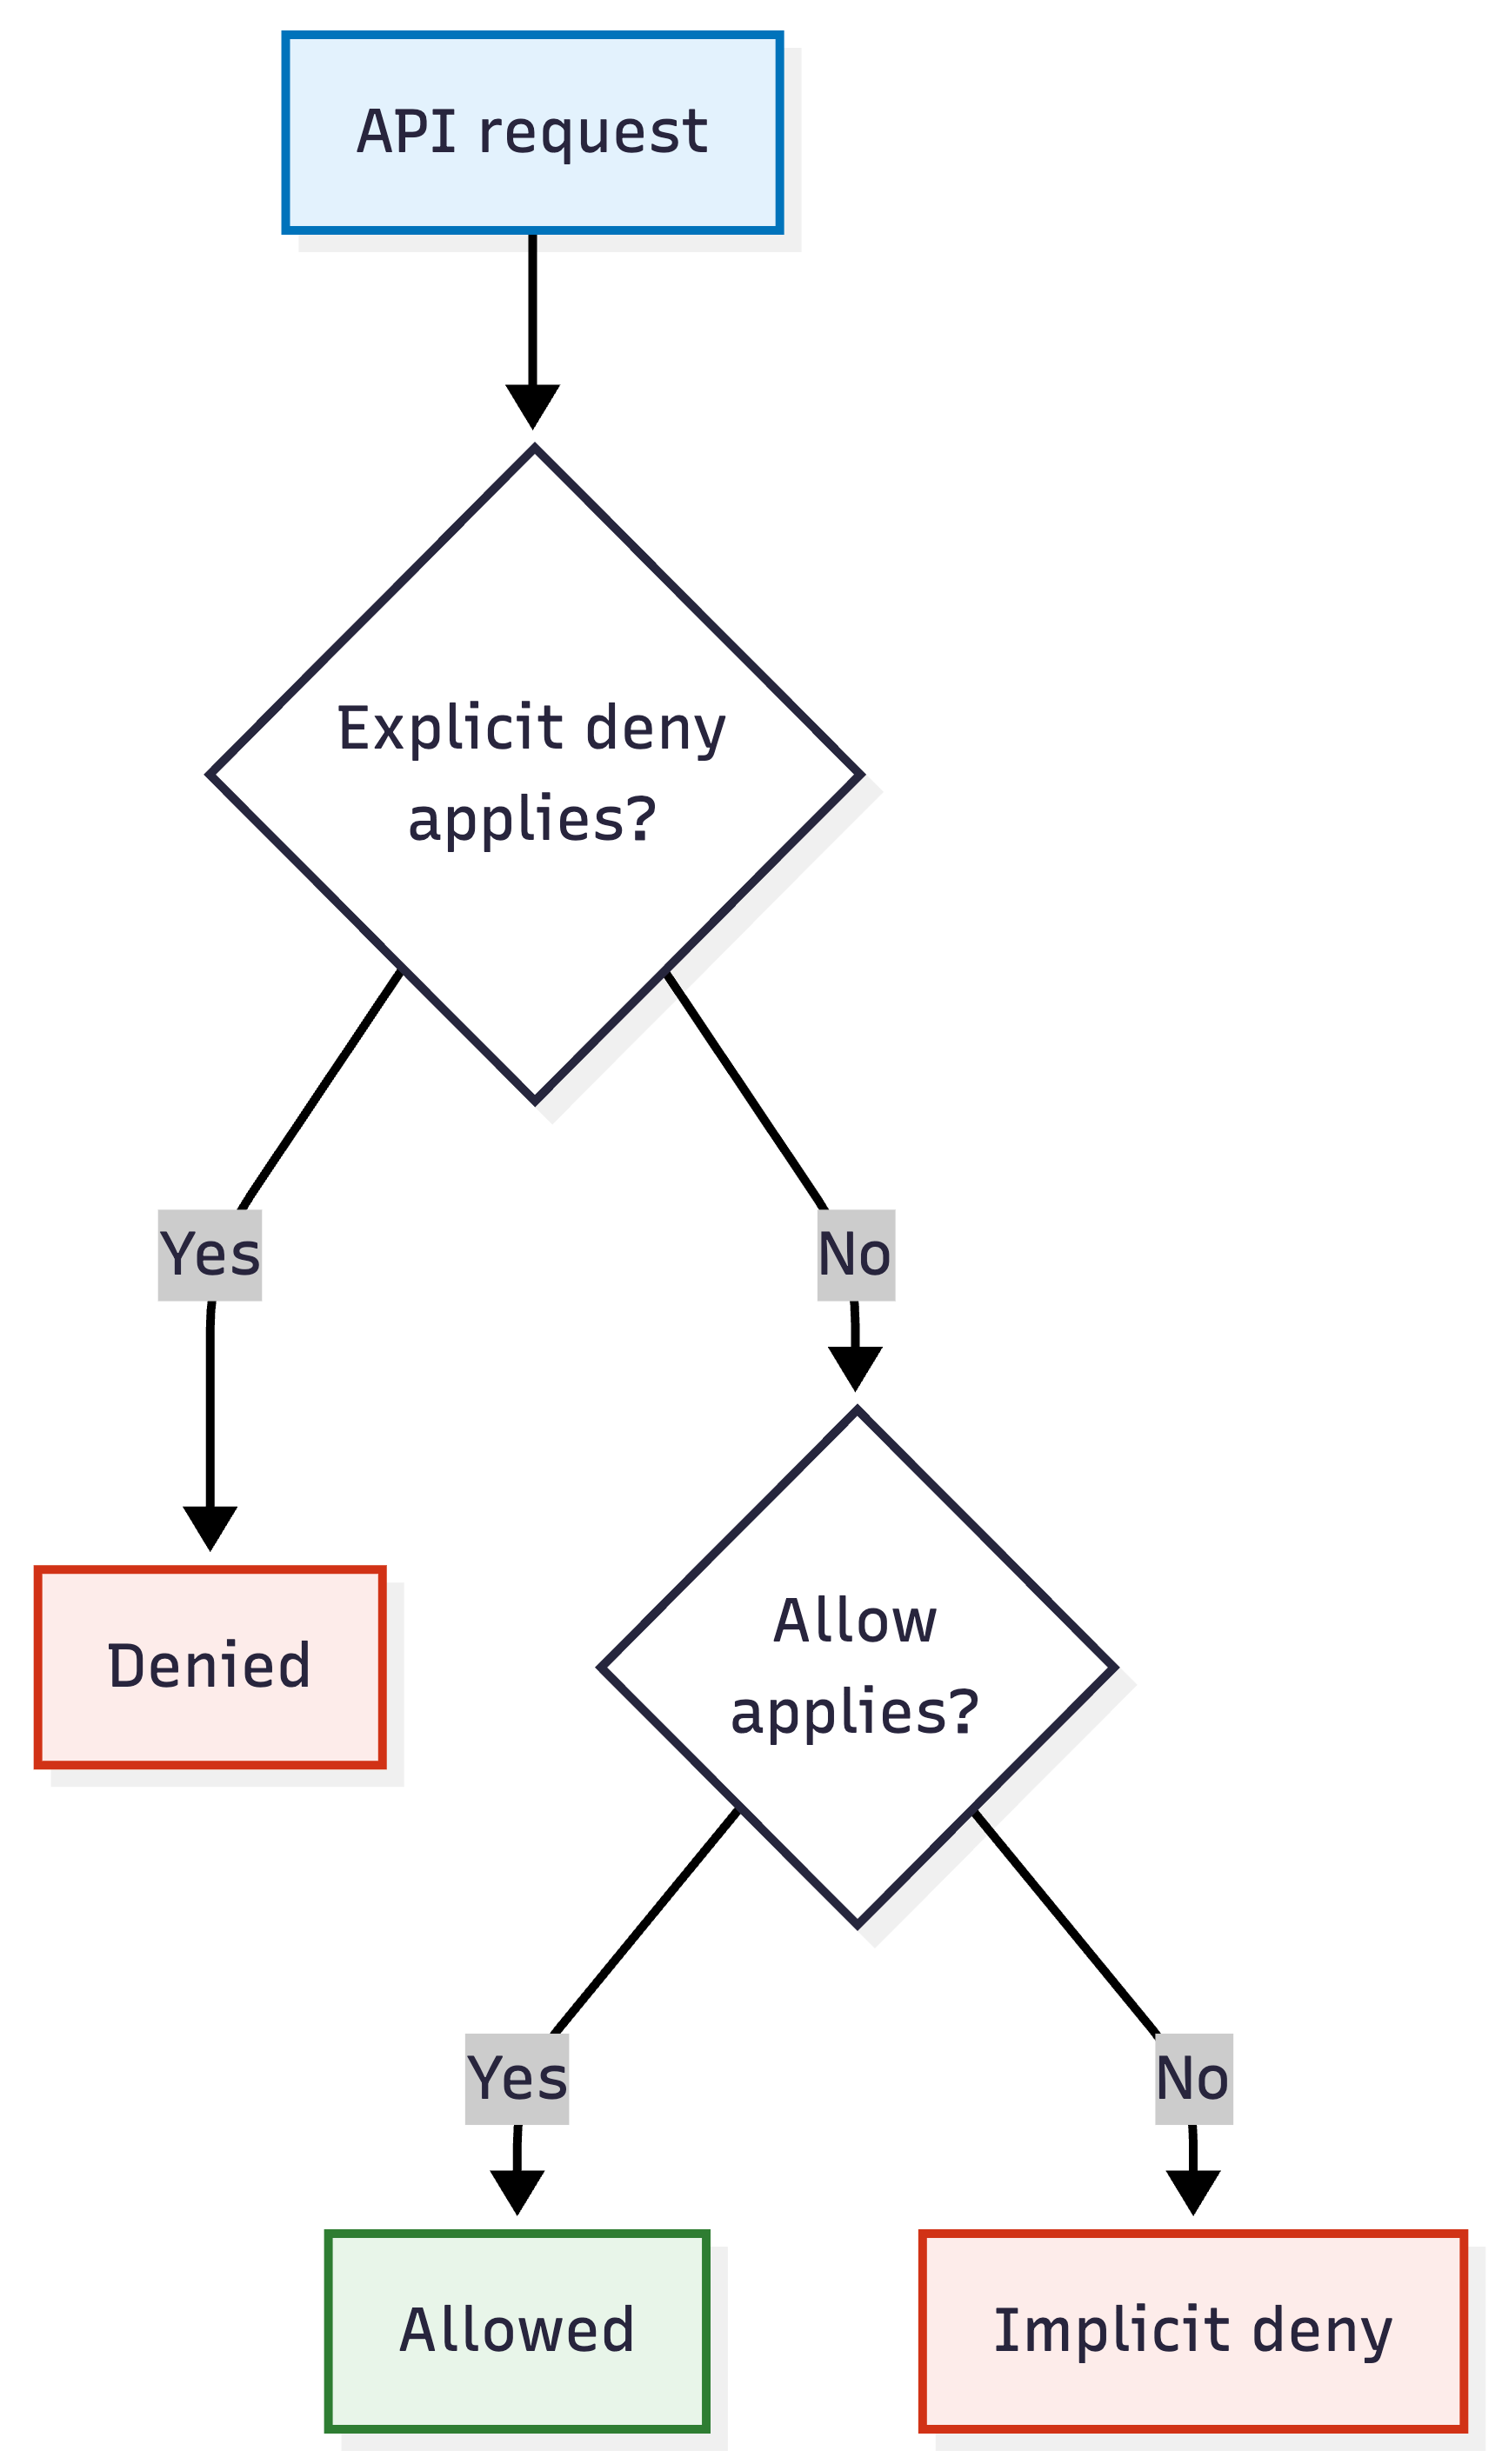
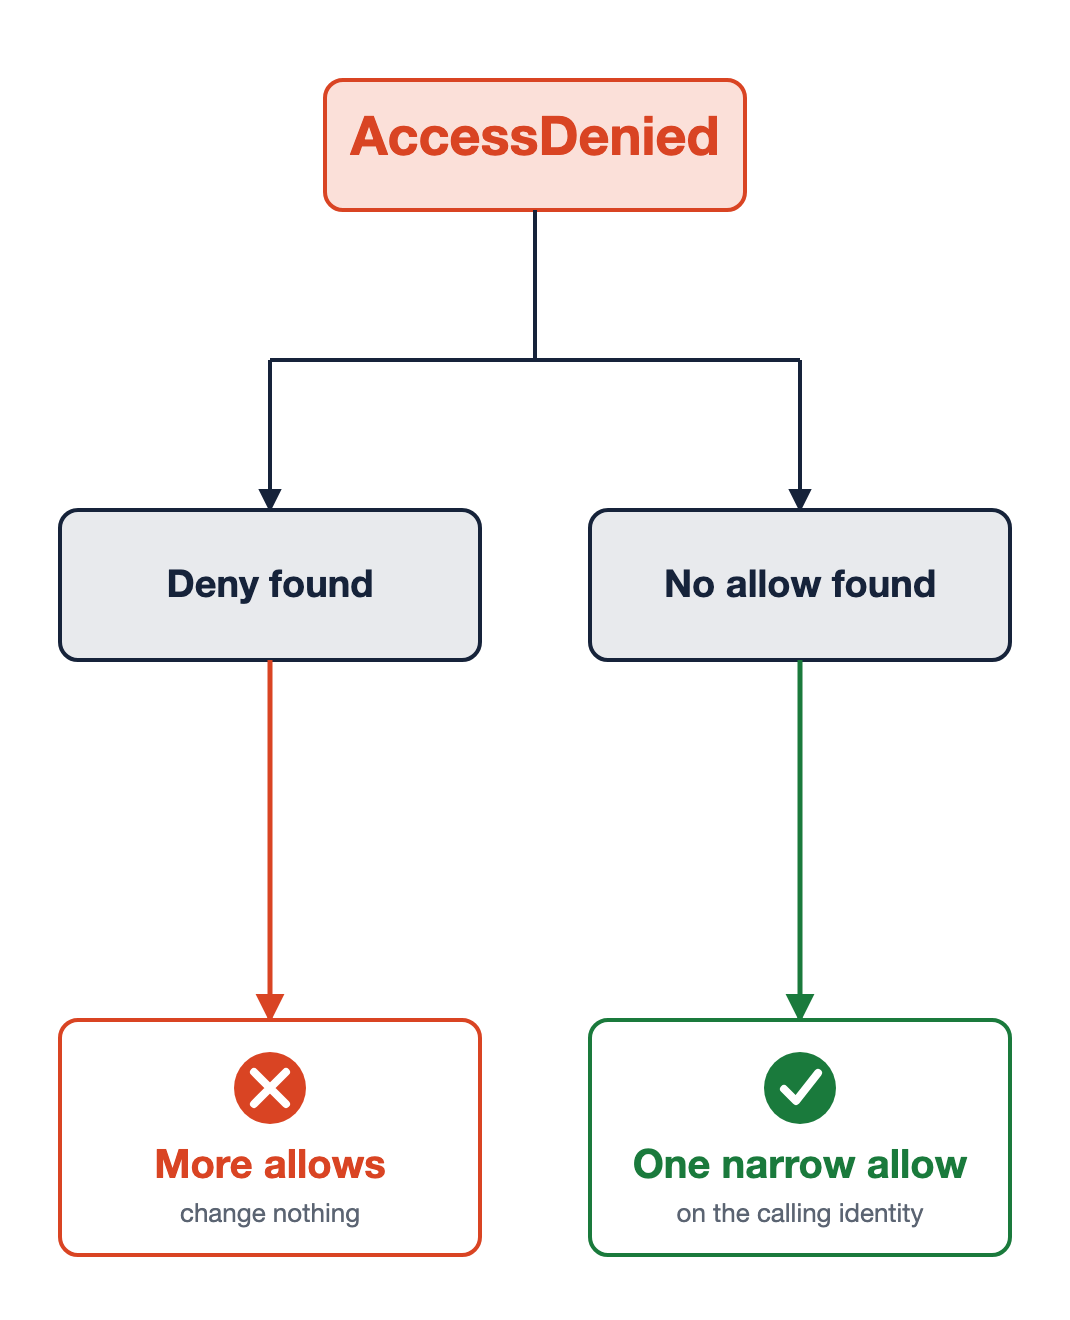
s3:GetObject → allow: geniş allow bunu kapsars3:DeleteObject → açık deny: bir ifade hayır diyorkms:Decrypt, dynamodb:GetItem → örtük deny: bu politika bu servislerden hiç bahsetmiyorAynı hata, iki neden
Açık deny
Örtük deny

Geliştiriciler için AWS Güvenliğini Kullanma