AWS Security 開發者實務
Rahul Singh
Technical Product Manager
{
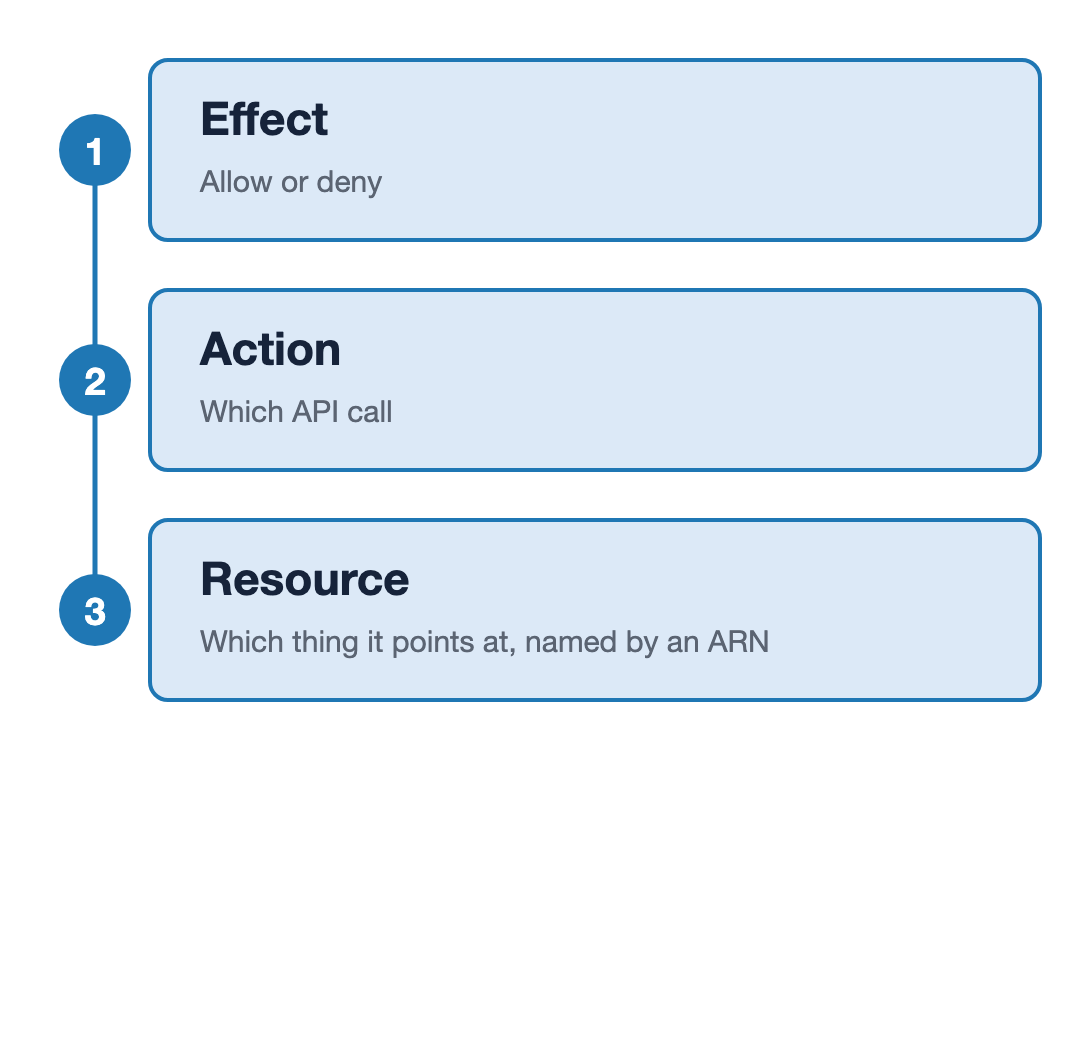
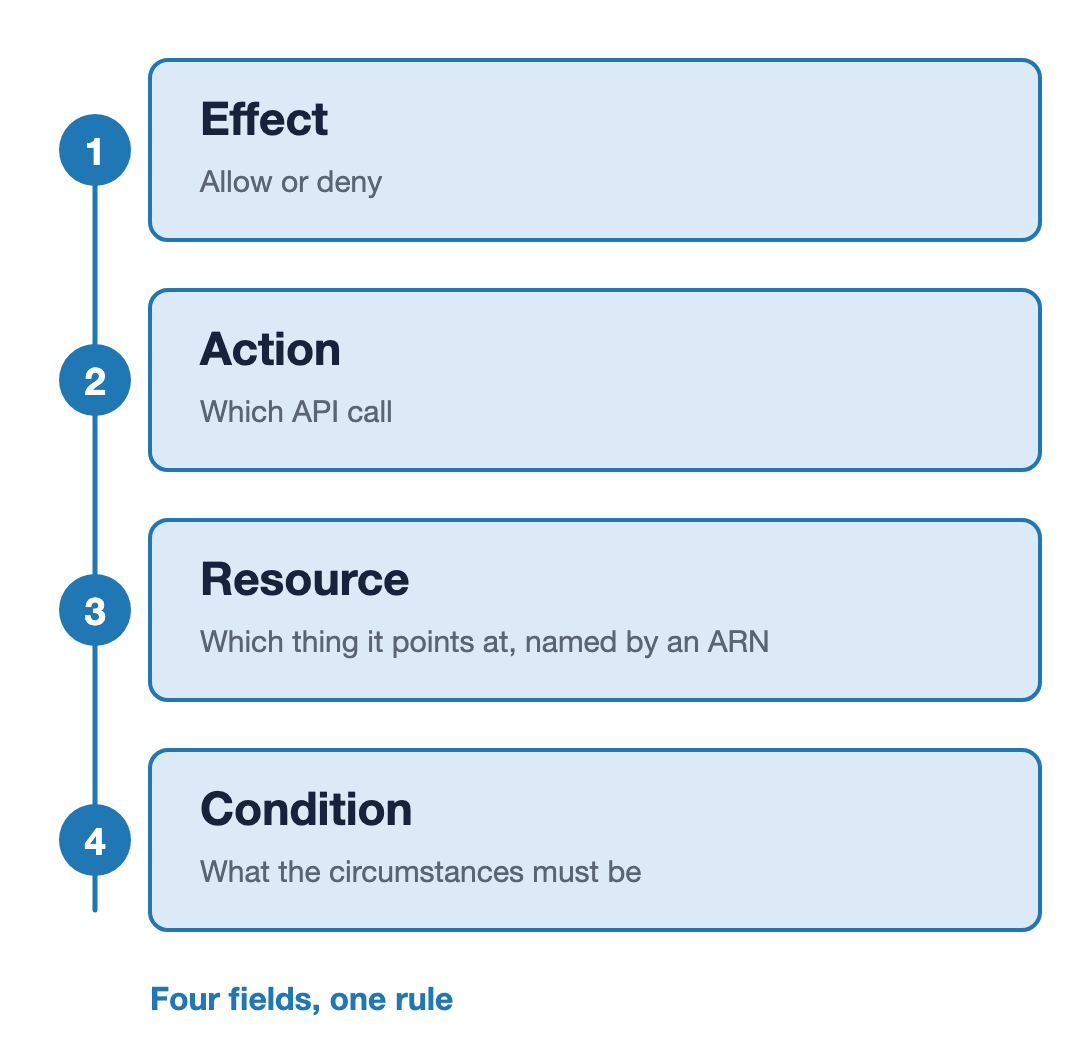
  "Effect": "Allow",
  "Action": "s3:GetObject",
  "Resource": "arn:aws:s3:::reports/*",
  "Condition": {
    "Bool": {
      "aws:SecureTransport": "true"
    },
    "IpAddress": {
      "aws:SourceIp": "203.0.113.0/24"
    }
  }
}
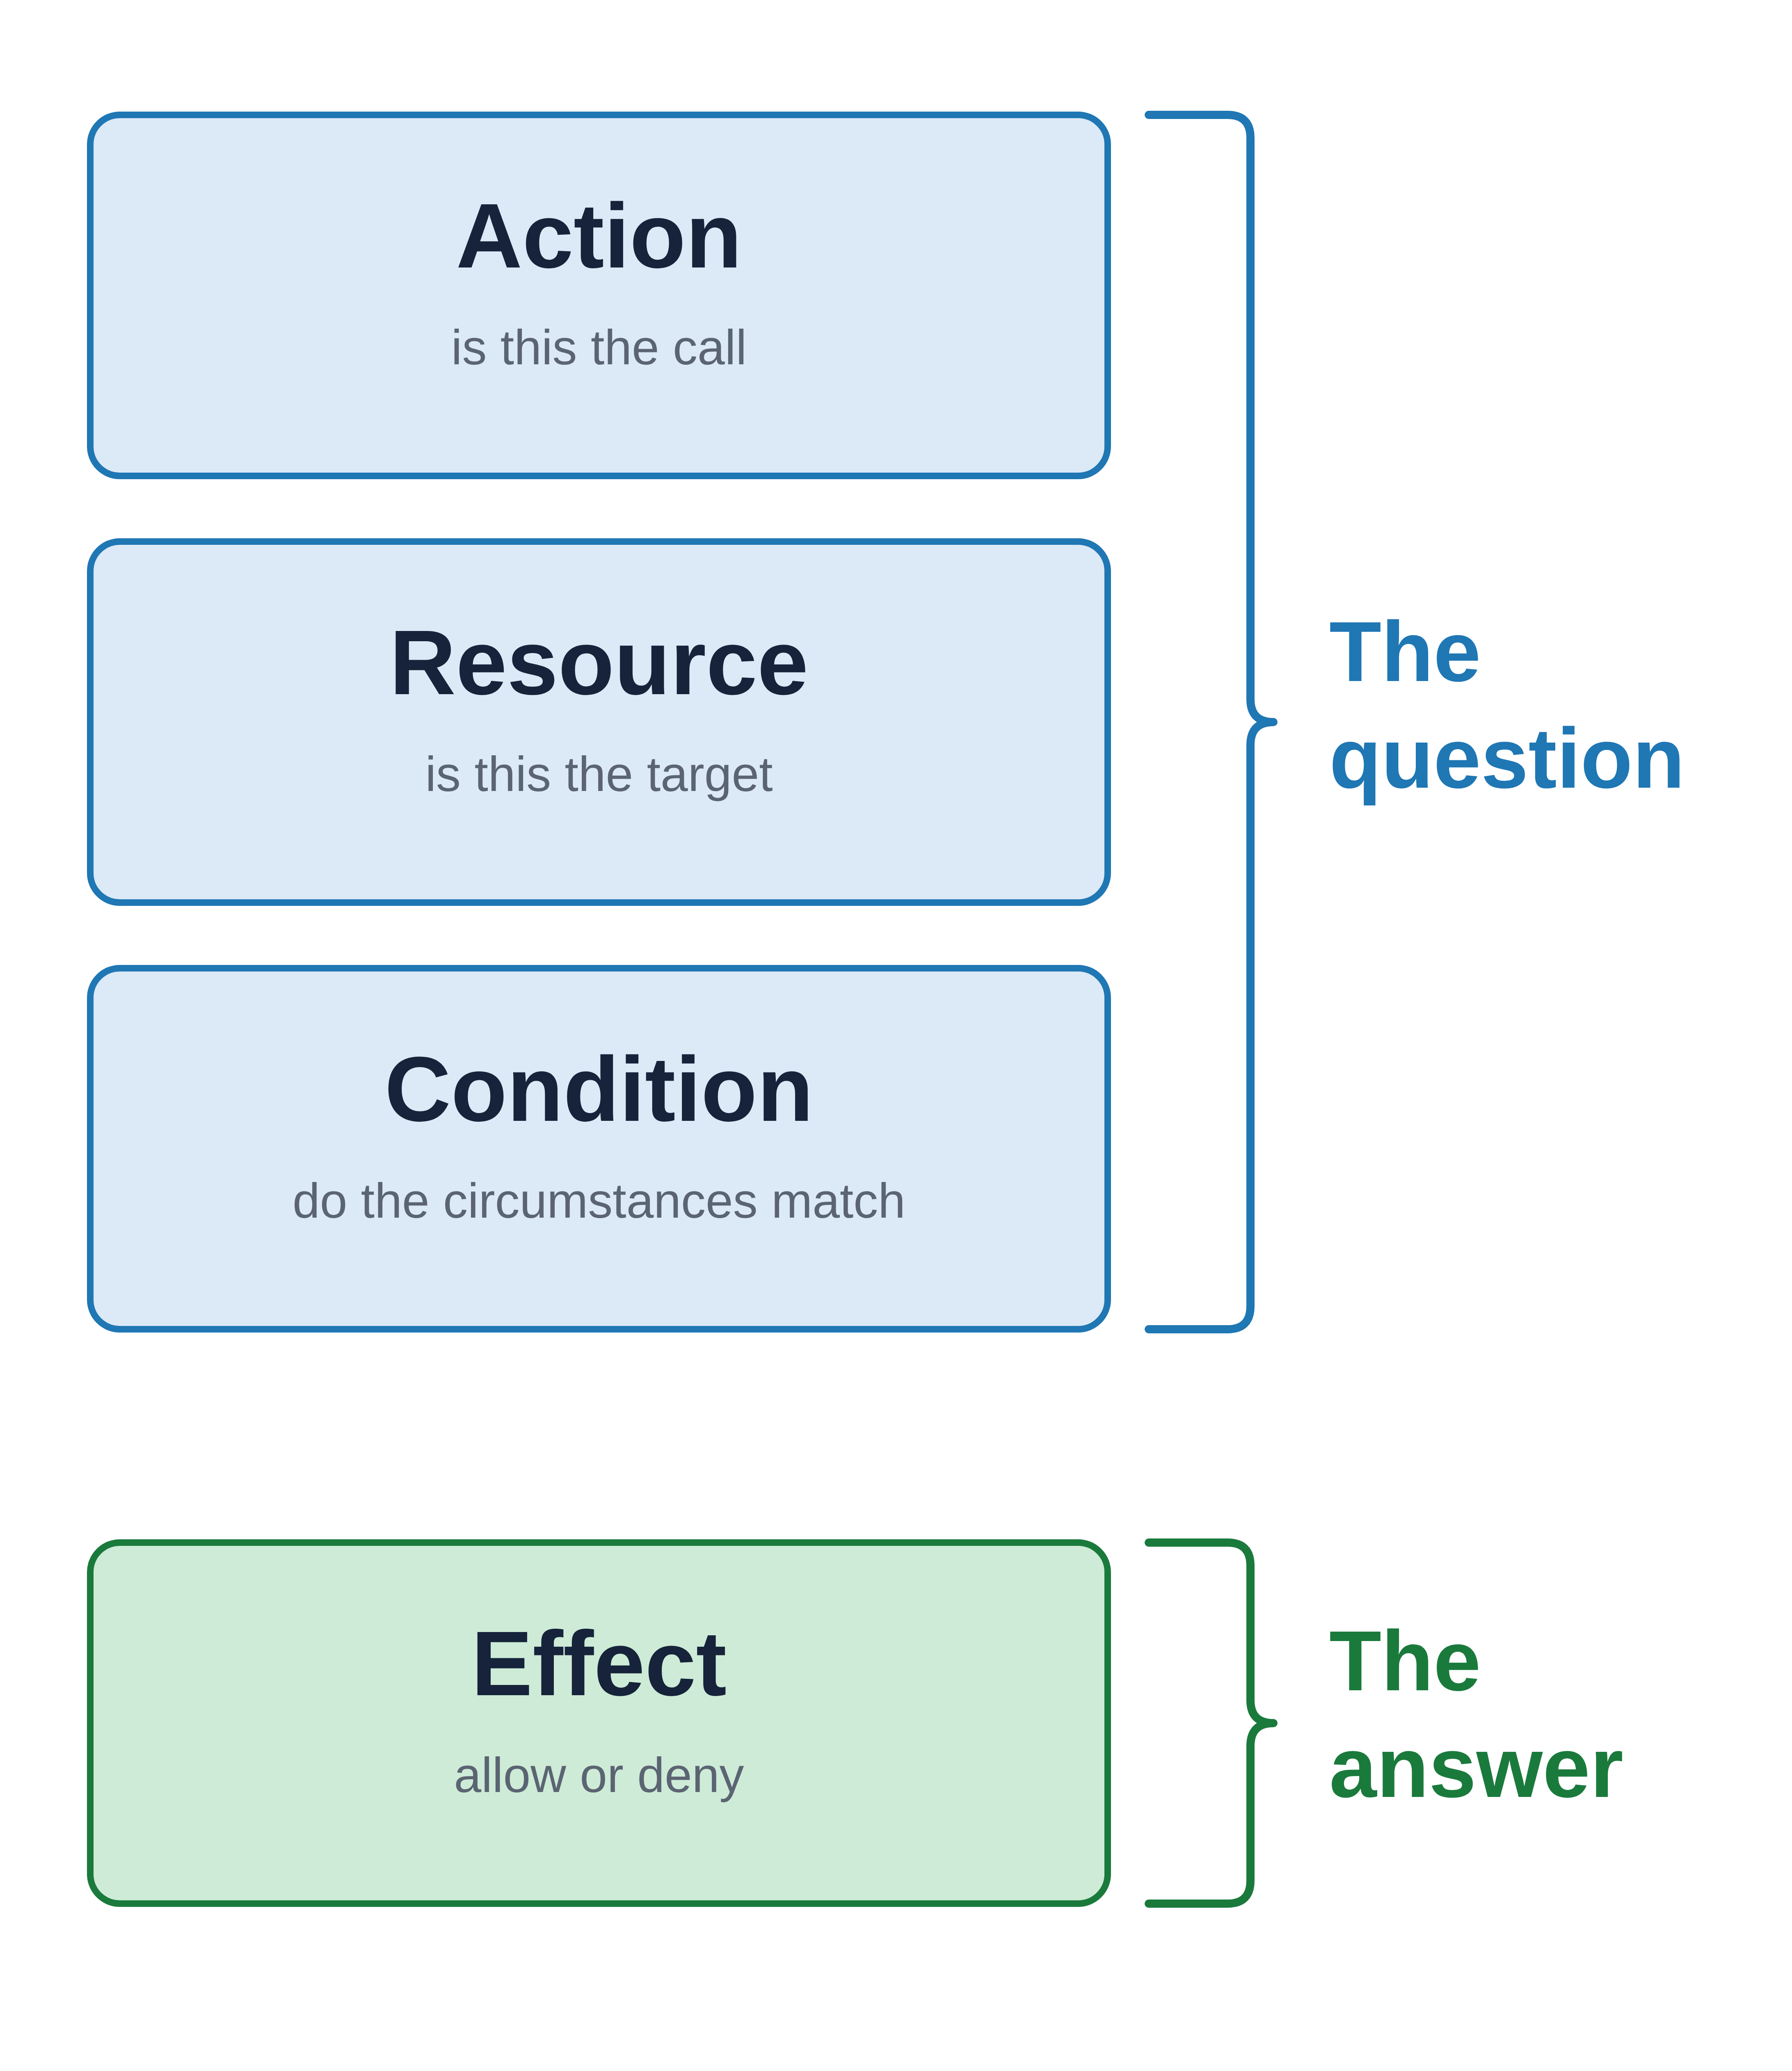
問題端
答案端
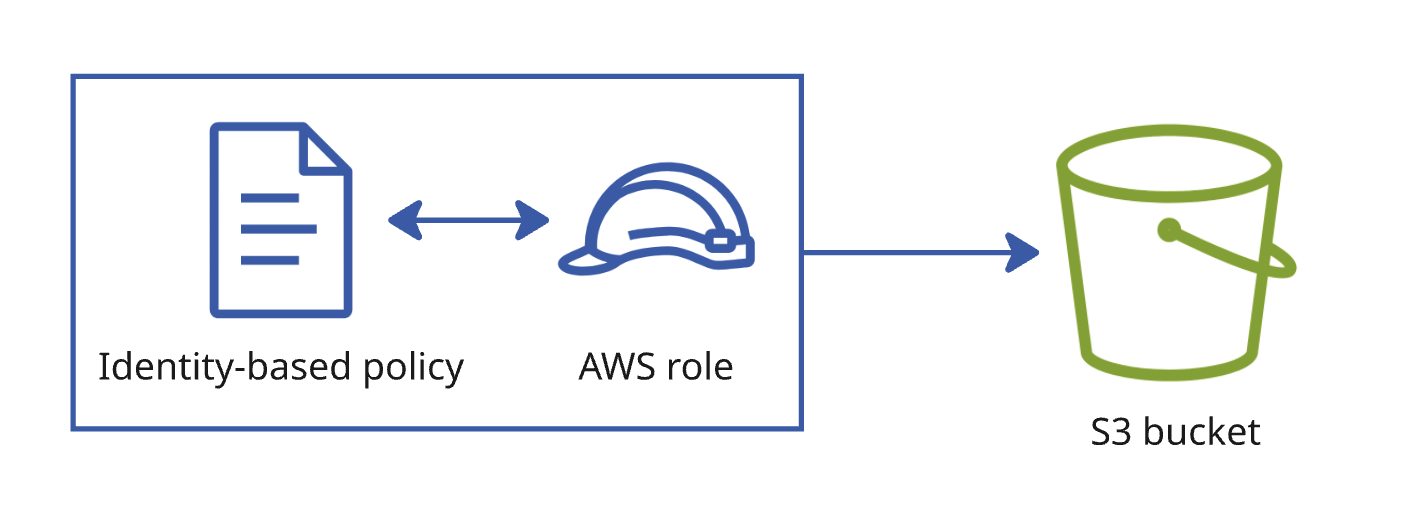
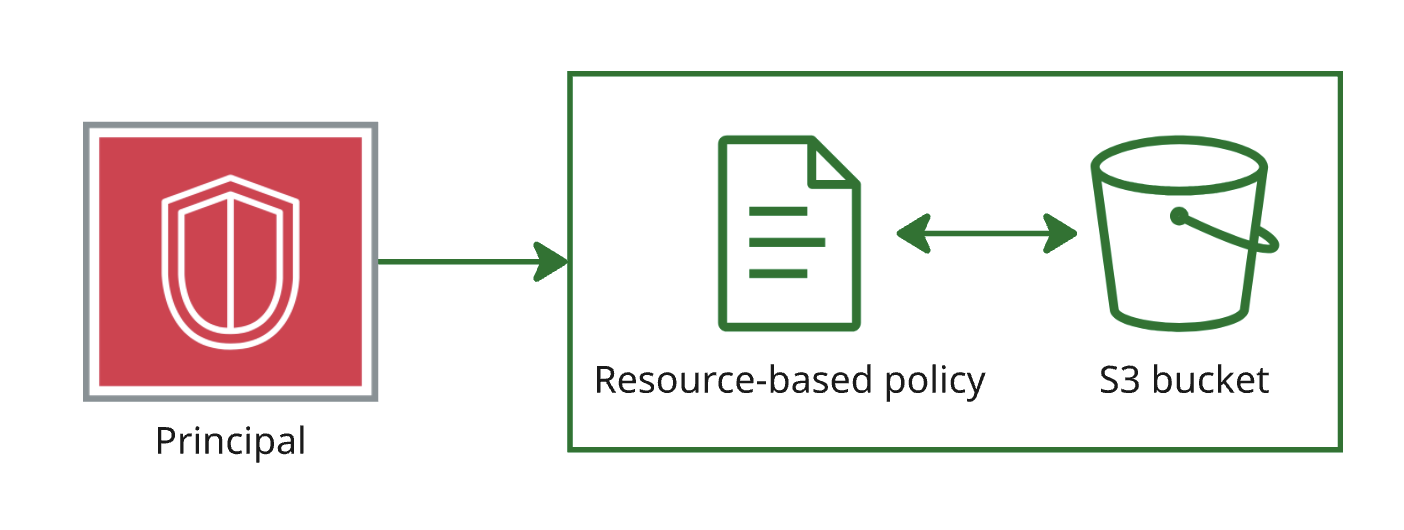
以身分為主(Identity-based)
以資源為主(Resource-based)
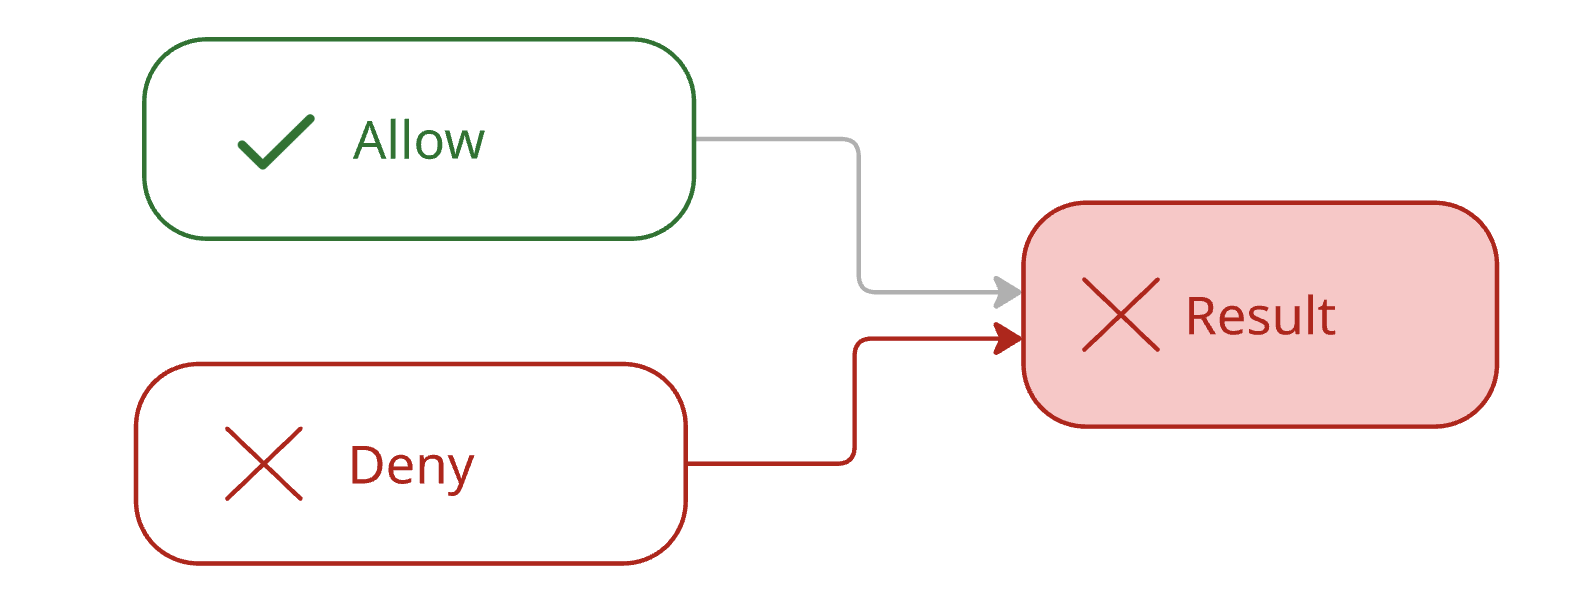
{"Effect": "Allow", "Action": "s3:*", "Resource": "*"}
{"Effect": "Deny",  "Action": "s3:DeleteObject", "Resource": "*"}
請求: s3:DeleteObject 的結果:Denied。
s3:DeleteObject
明確拒絕優先於任何允許,再廣也一樣
s3:GetObject
kms:Decrypt
dynamodb:GetItem
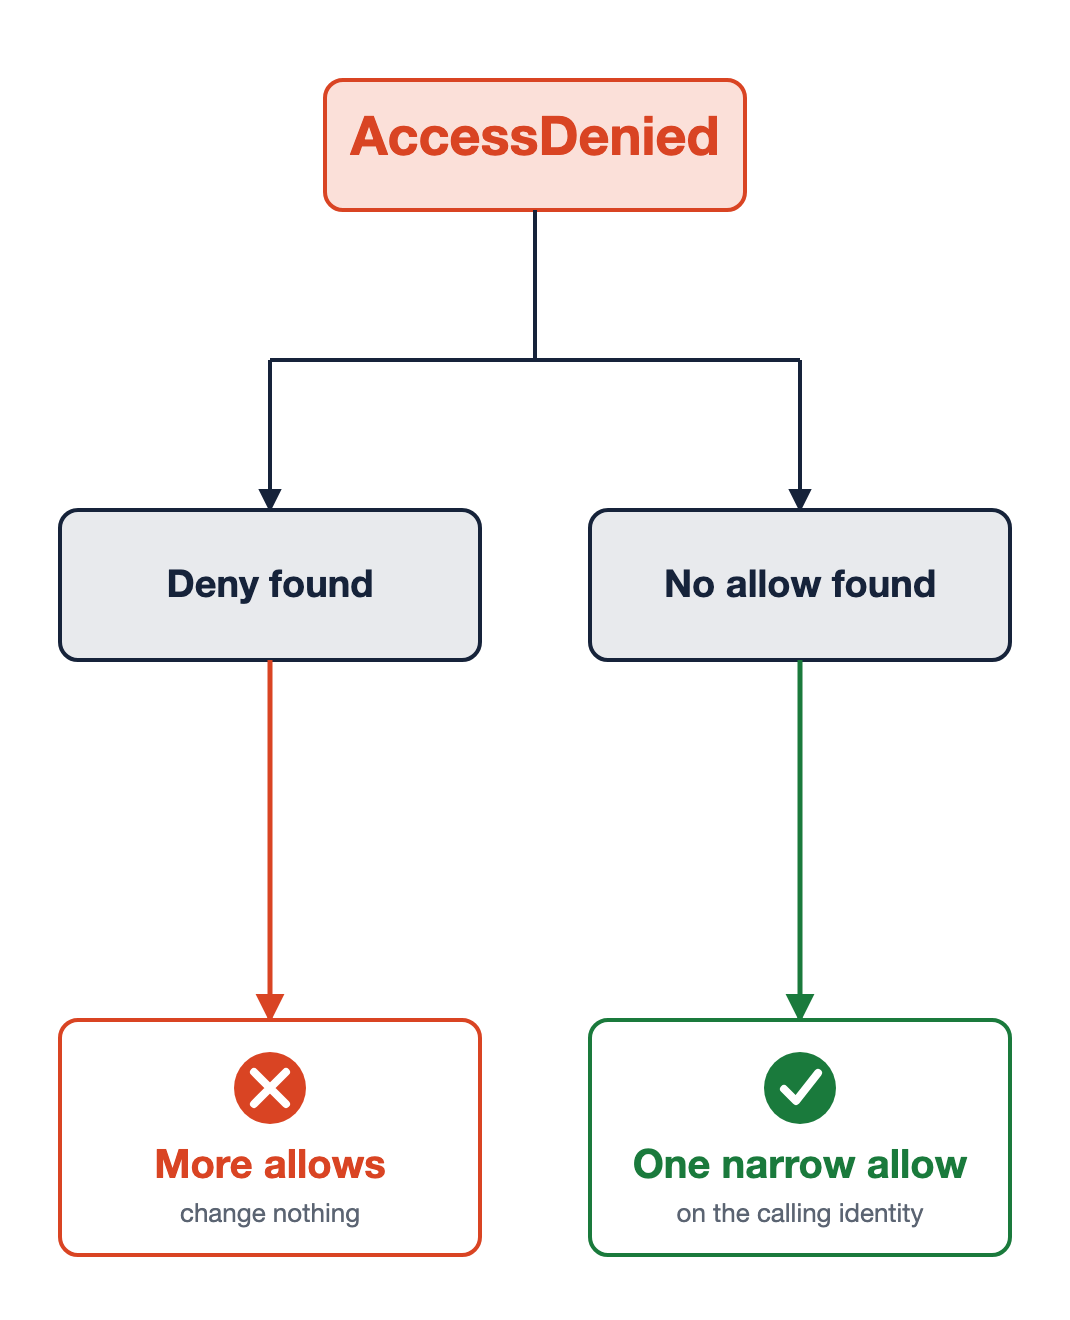
同樣錯誤,兩種成因
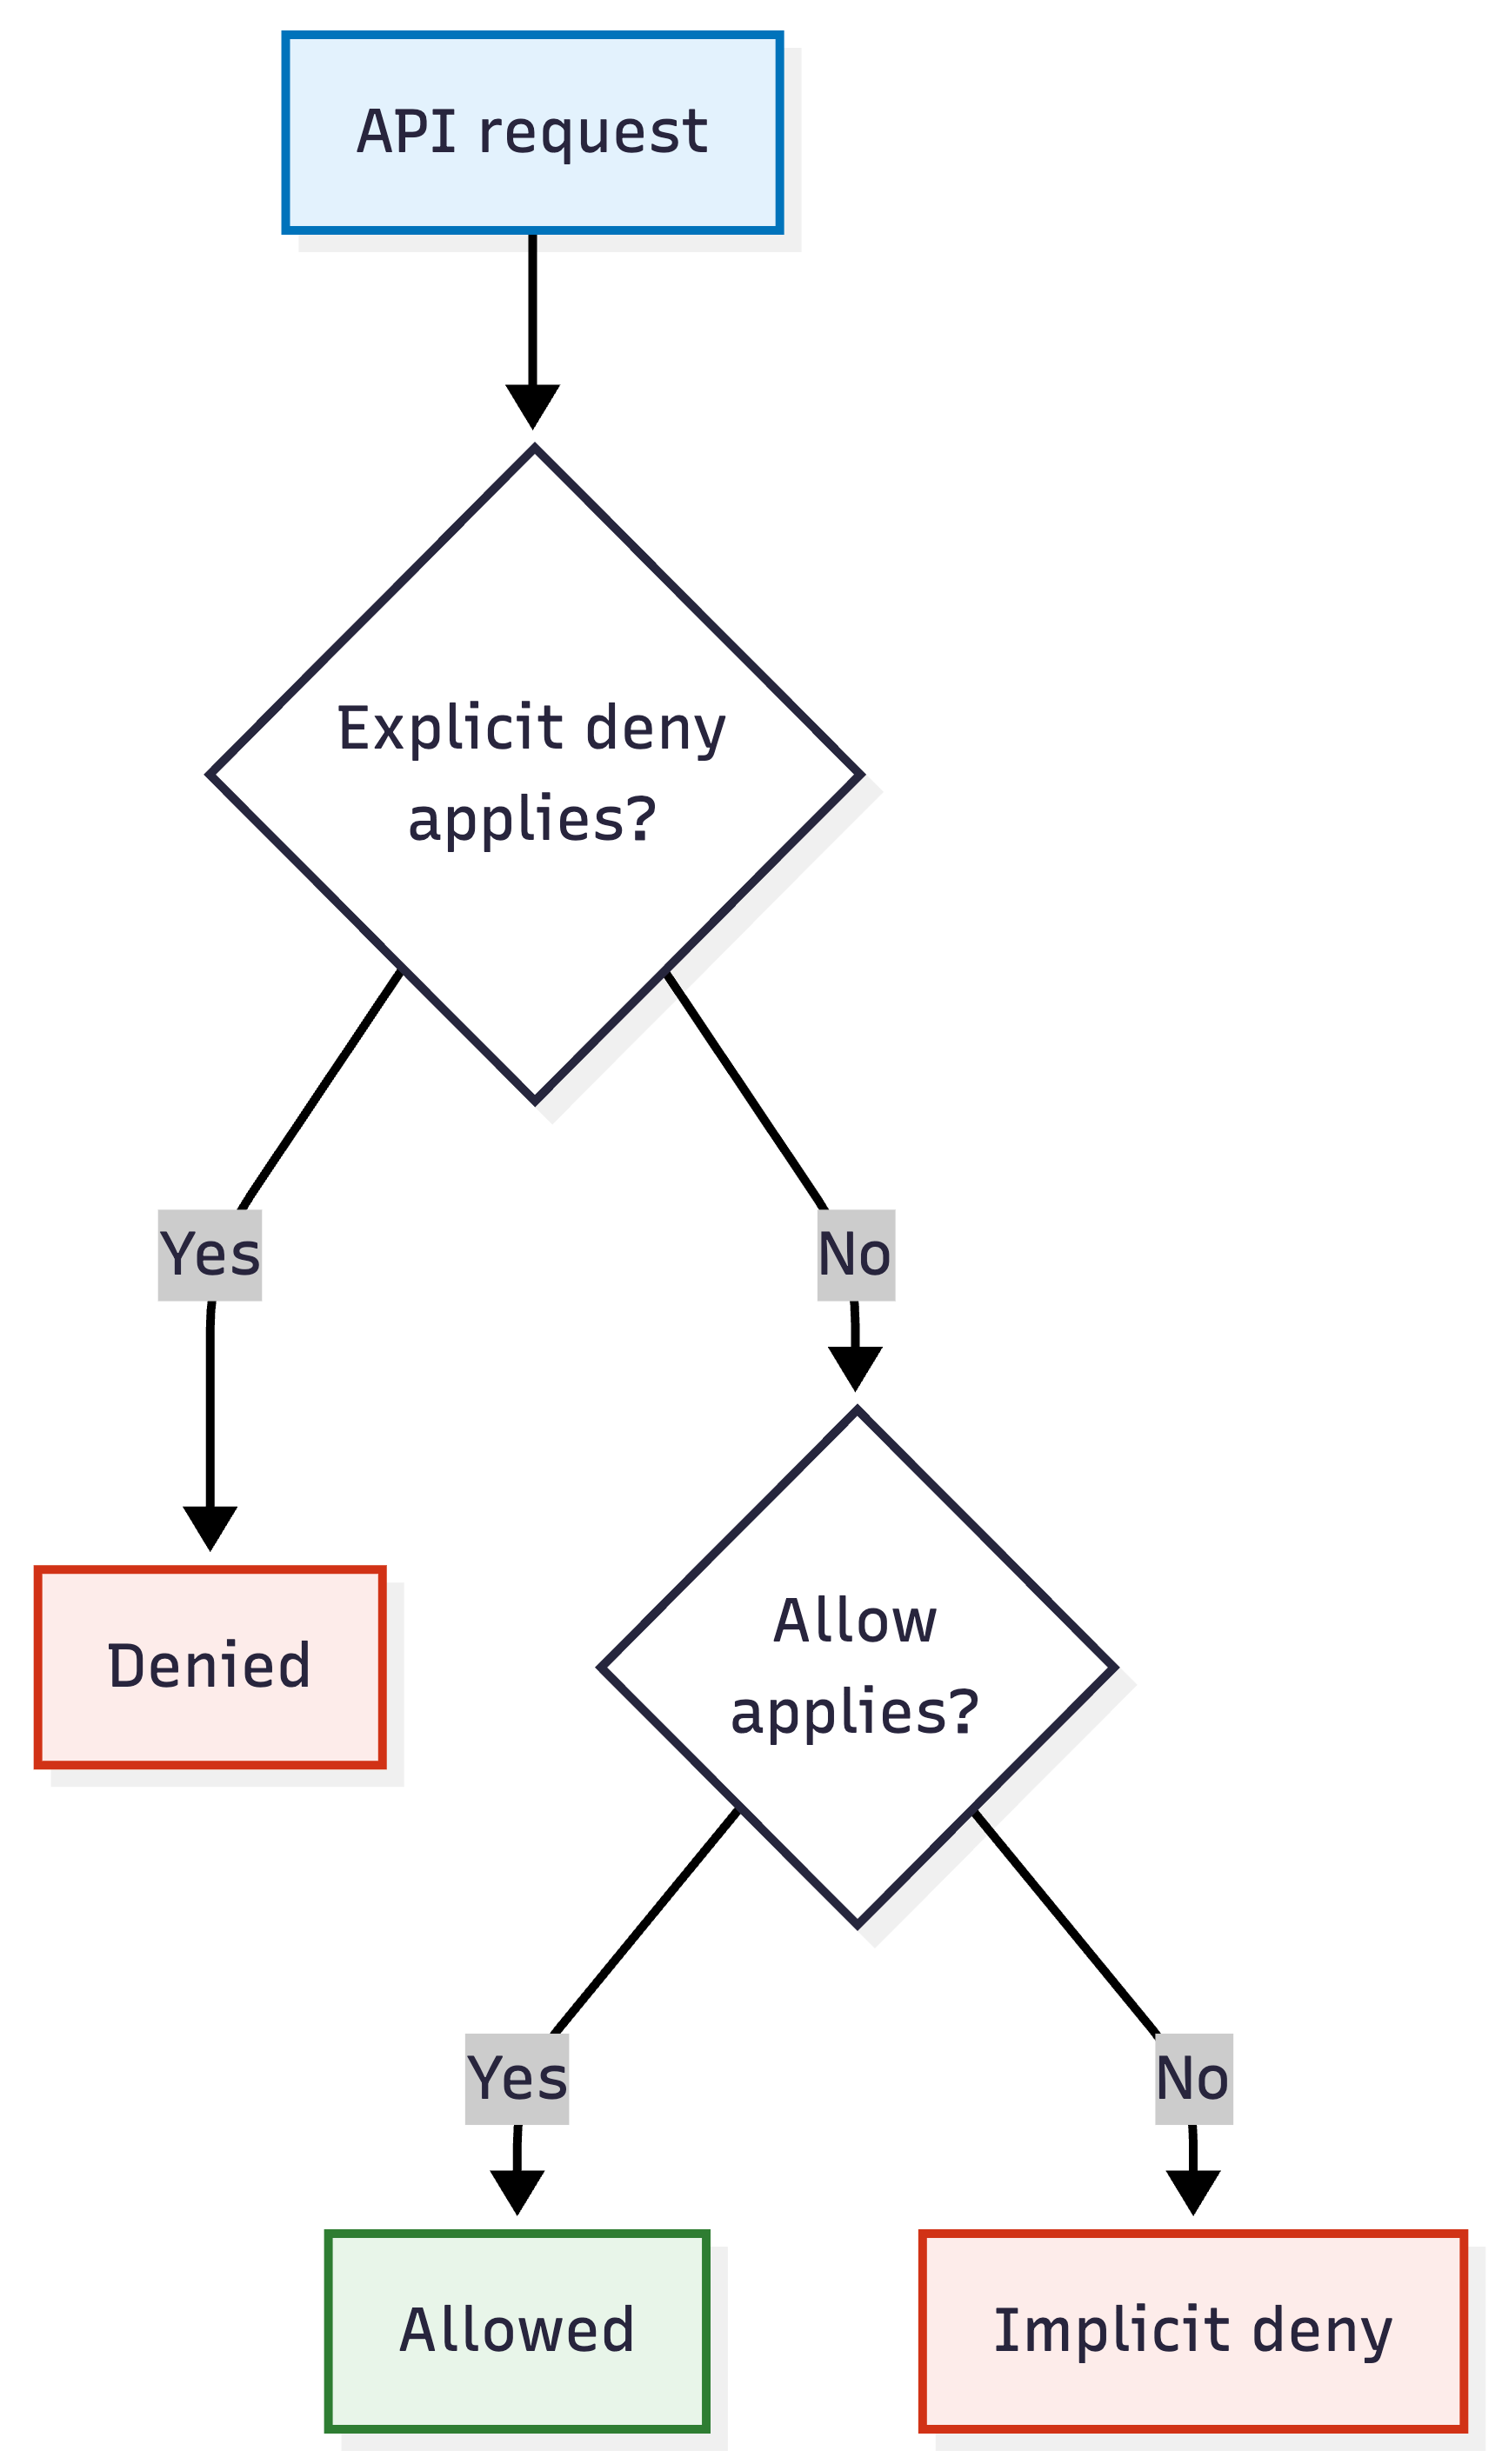
明確拒絕
隱含拒絕