डेवलपर्स के लिए AWS Security का उपयोग
Rahul Singh
Technical Product Manager
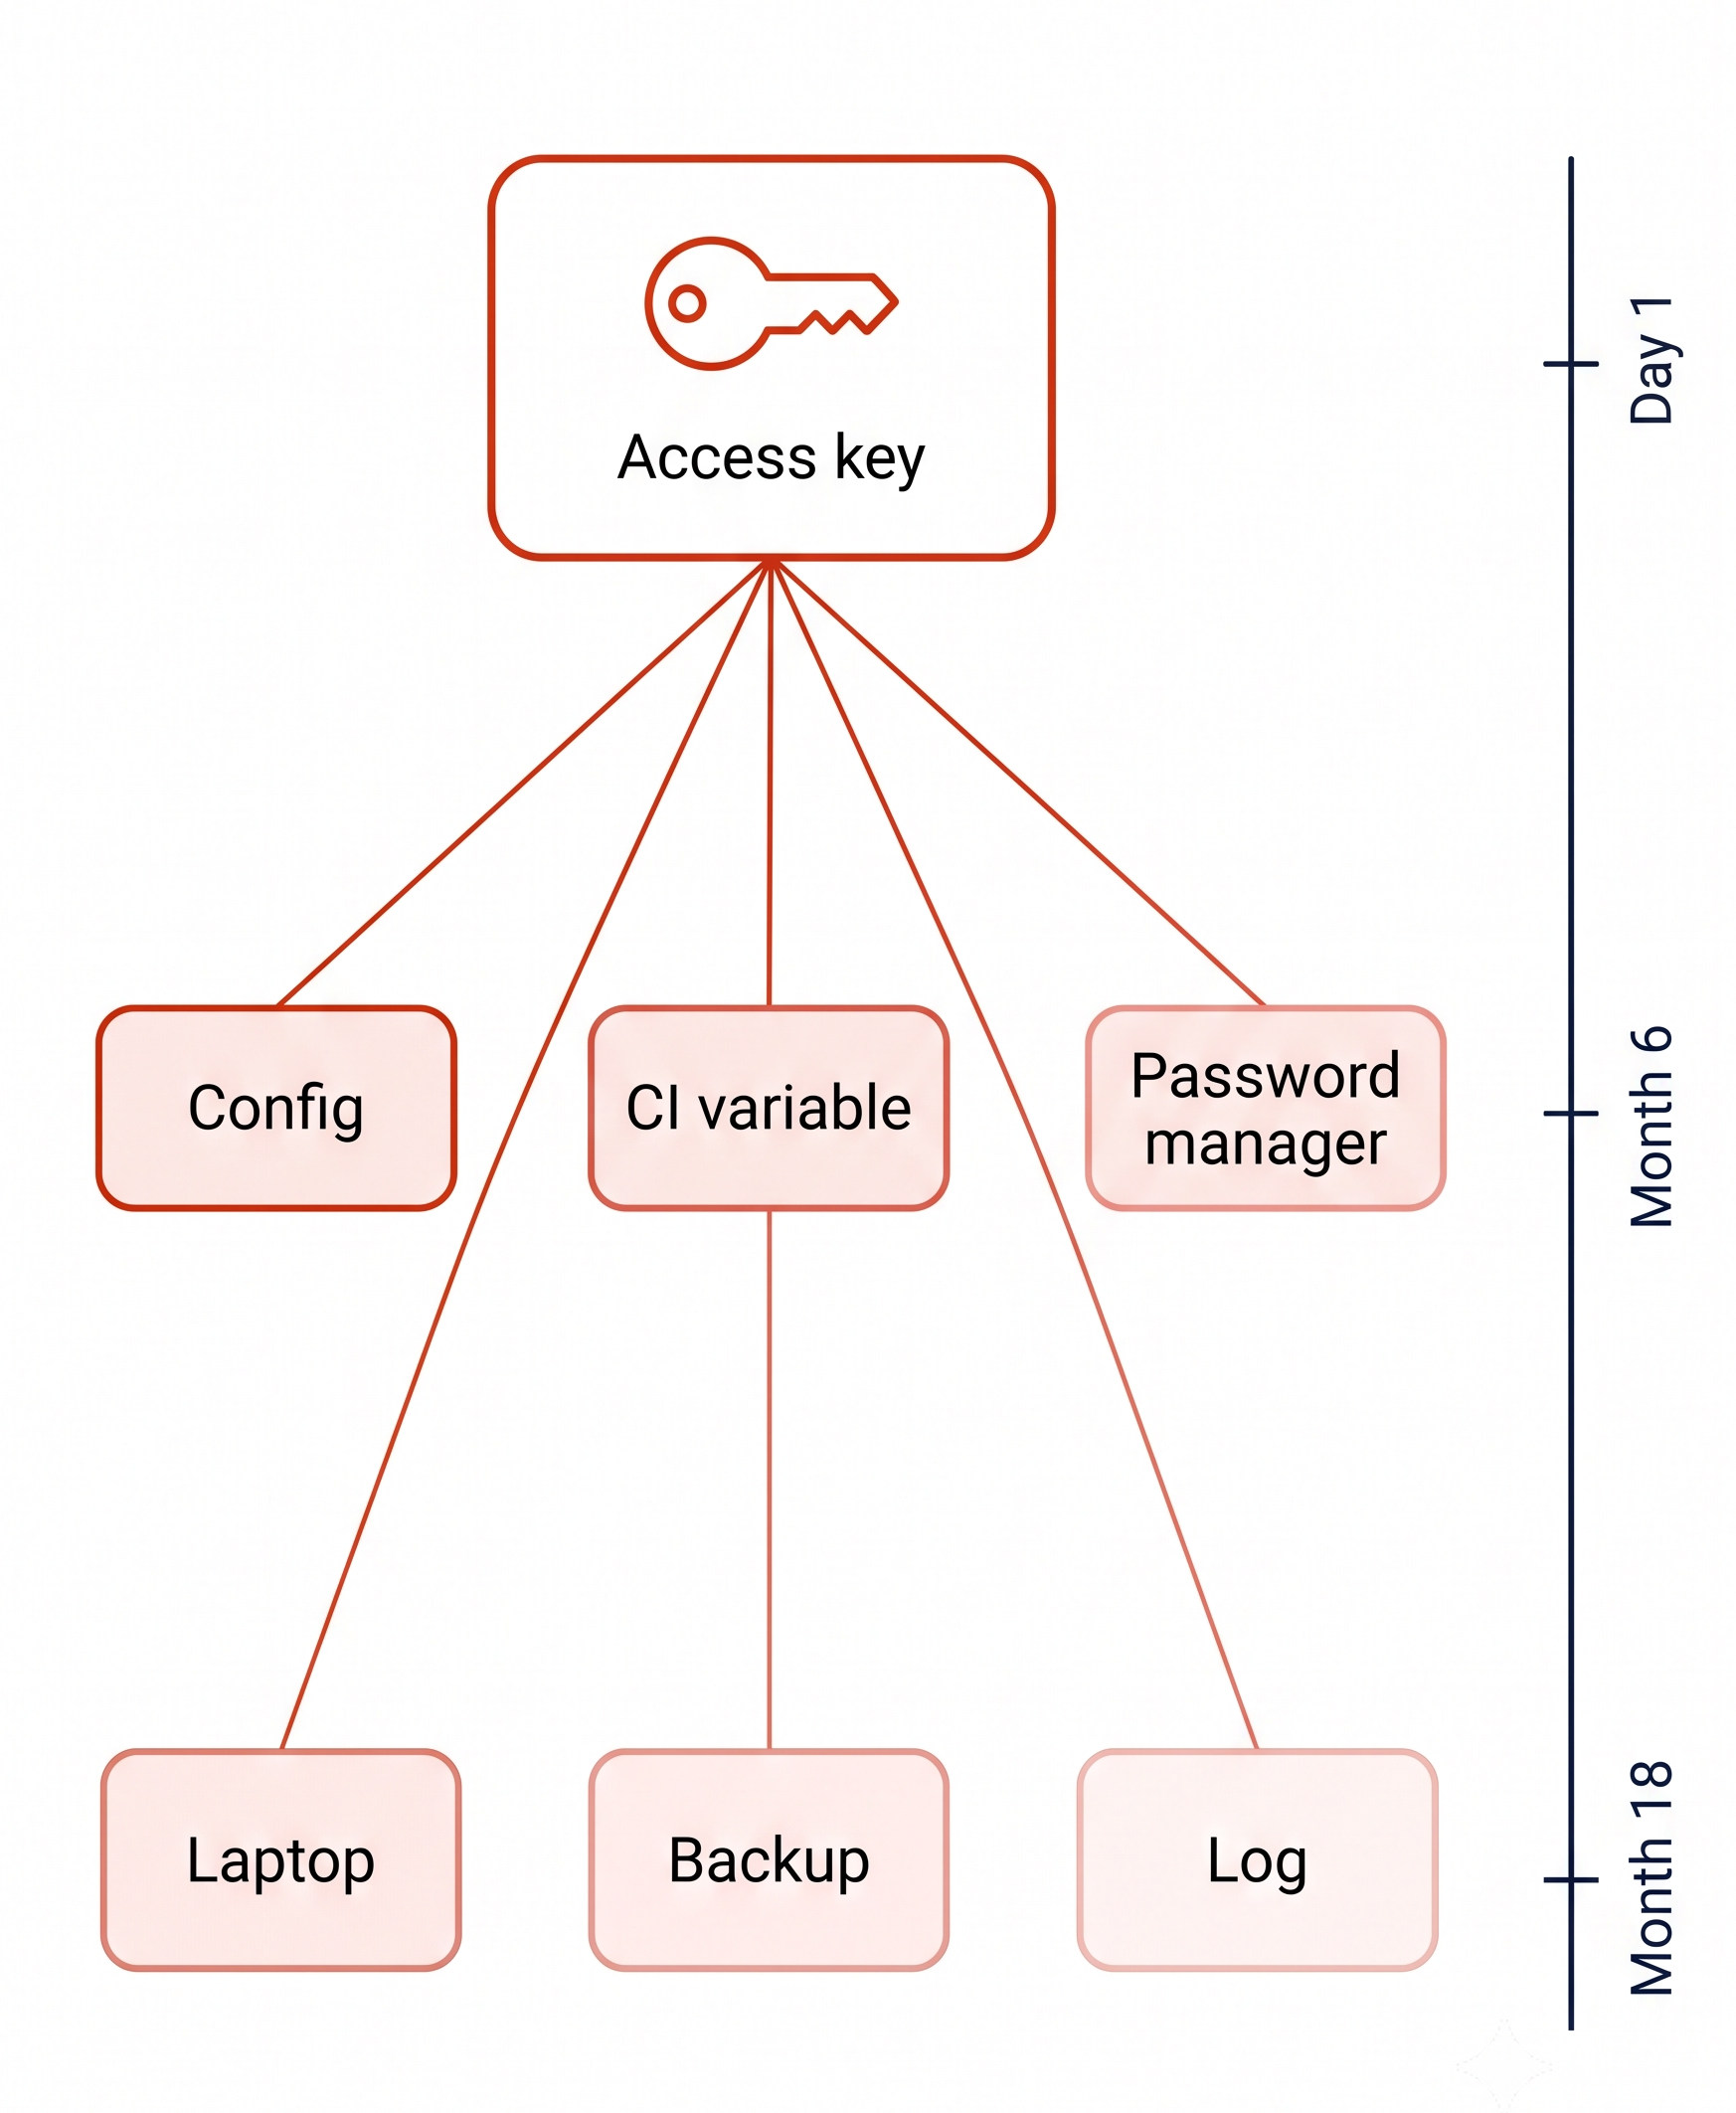
काम तेज करने के लिए, एक key स्क्रिप्ट में बनाई जाती है और एक configuration फ़ाइल में रखी जाती है.
फ़ाइल के अंदर यह:

काम तेज करने के लिए, एक key स्क्रिप्ट में बनाई जाती है और एक configuration फ़ाइल में रखी जाती है.
फ़ाइल के अंदर यह:
18 महीनों बाद भी यह मान्य है

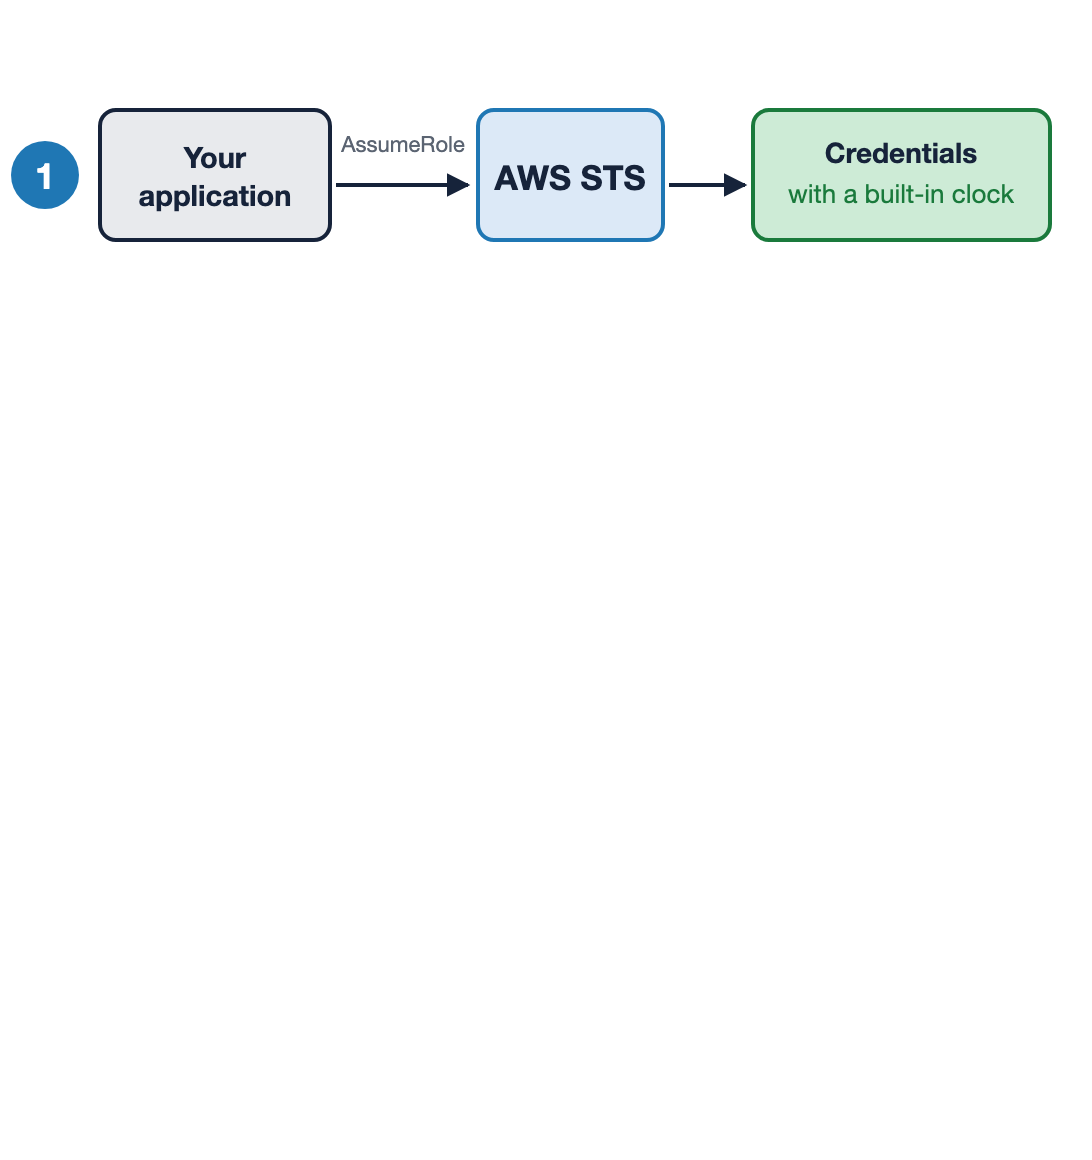
AWS STS के साथ expiry को default बनाएँ
एक role माँगें, built-in clock वाले credentials पाएँ
Security Token Service (STS): expiry जुड़ा होता है, डिफ़ॉल्ट एक घंटा

AWS STS के साथ expiry को default बनाएँ
एक role माँगें, built-in clock वाले credentials पाएँ
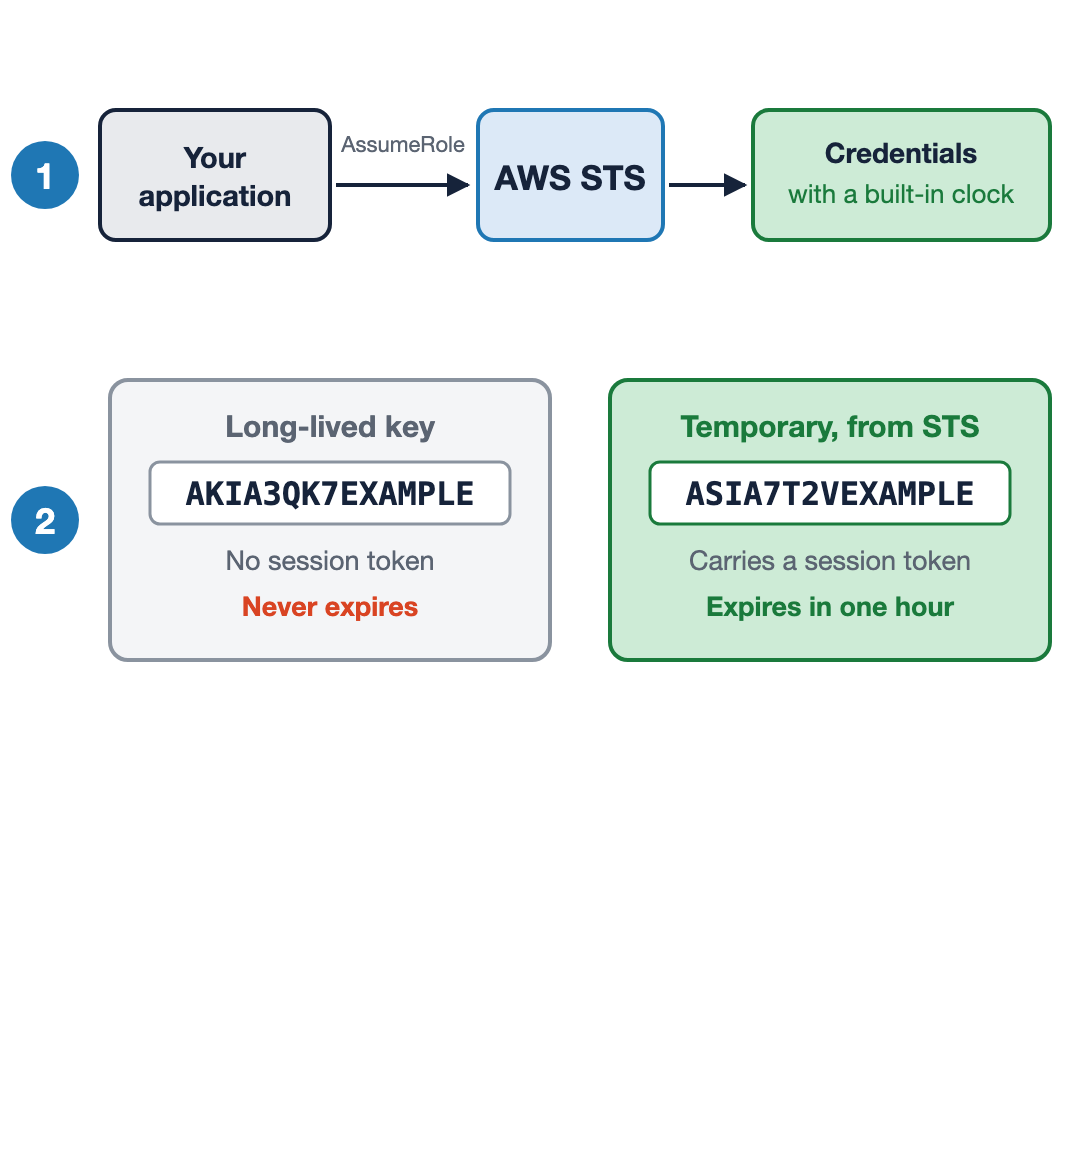
अस्थायी credentials ASIA से शुरू होते हैं और session token रखते हैं
Security Token Service (STS): expiry जुड़ा होता है, डिफ़ॉल्ट एक घंटा

AWS STS के साथ expiry को default बनाएँ
एक role माँगें, built-in clock वाले credentials पाएँ
अस्थायी credentials ASIA से शुरू होते हैं और session token रखते हैं
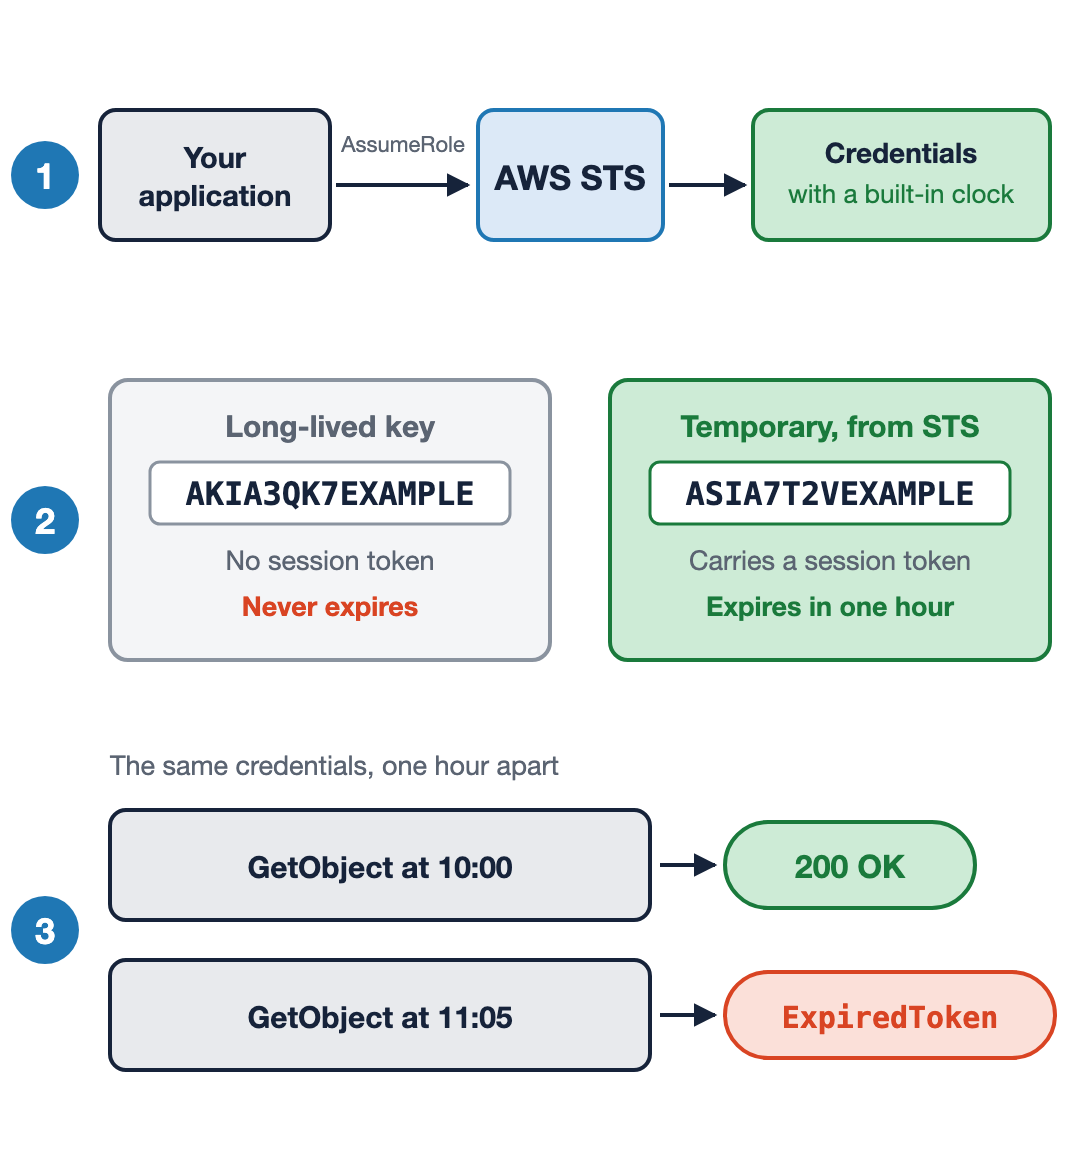
वही call पहले स्वीकार होती है, फिर नहीं
Security Token Service (STS): expiry जुड़ा होता है, डिफ़ॉल्ट एक घंटा

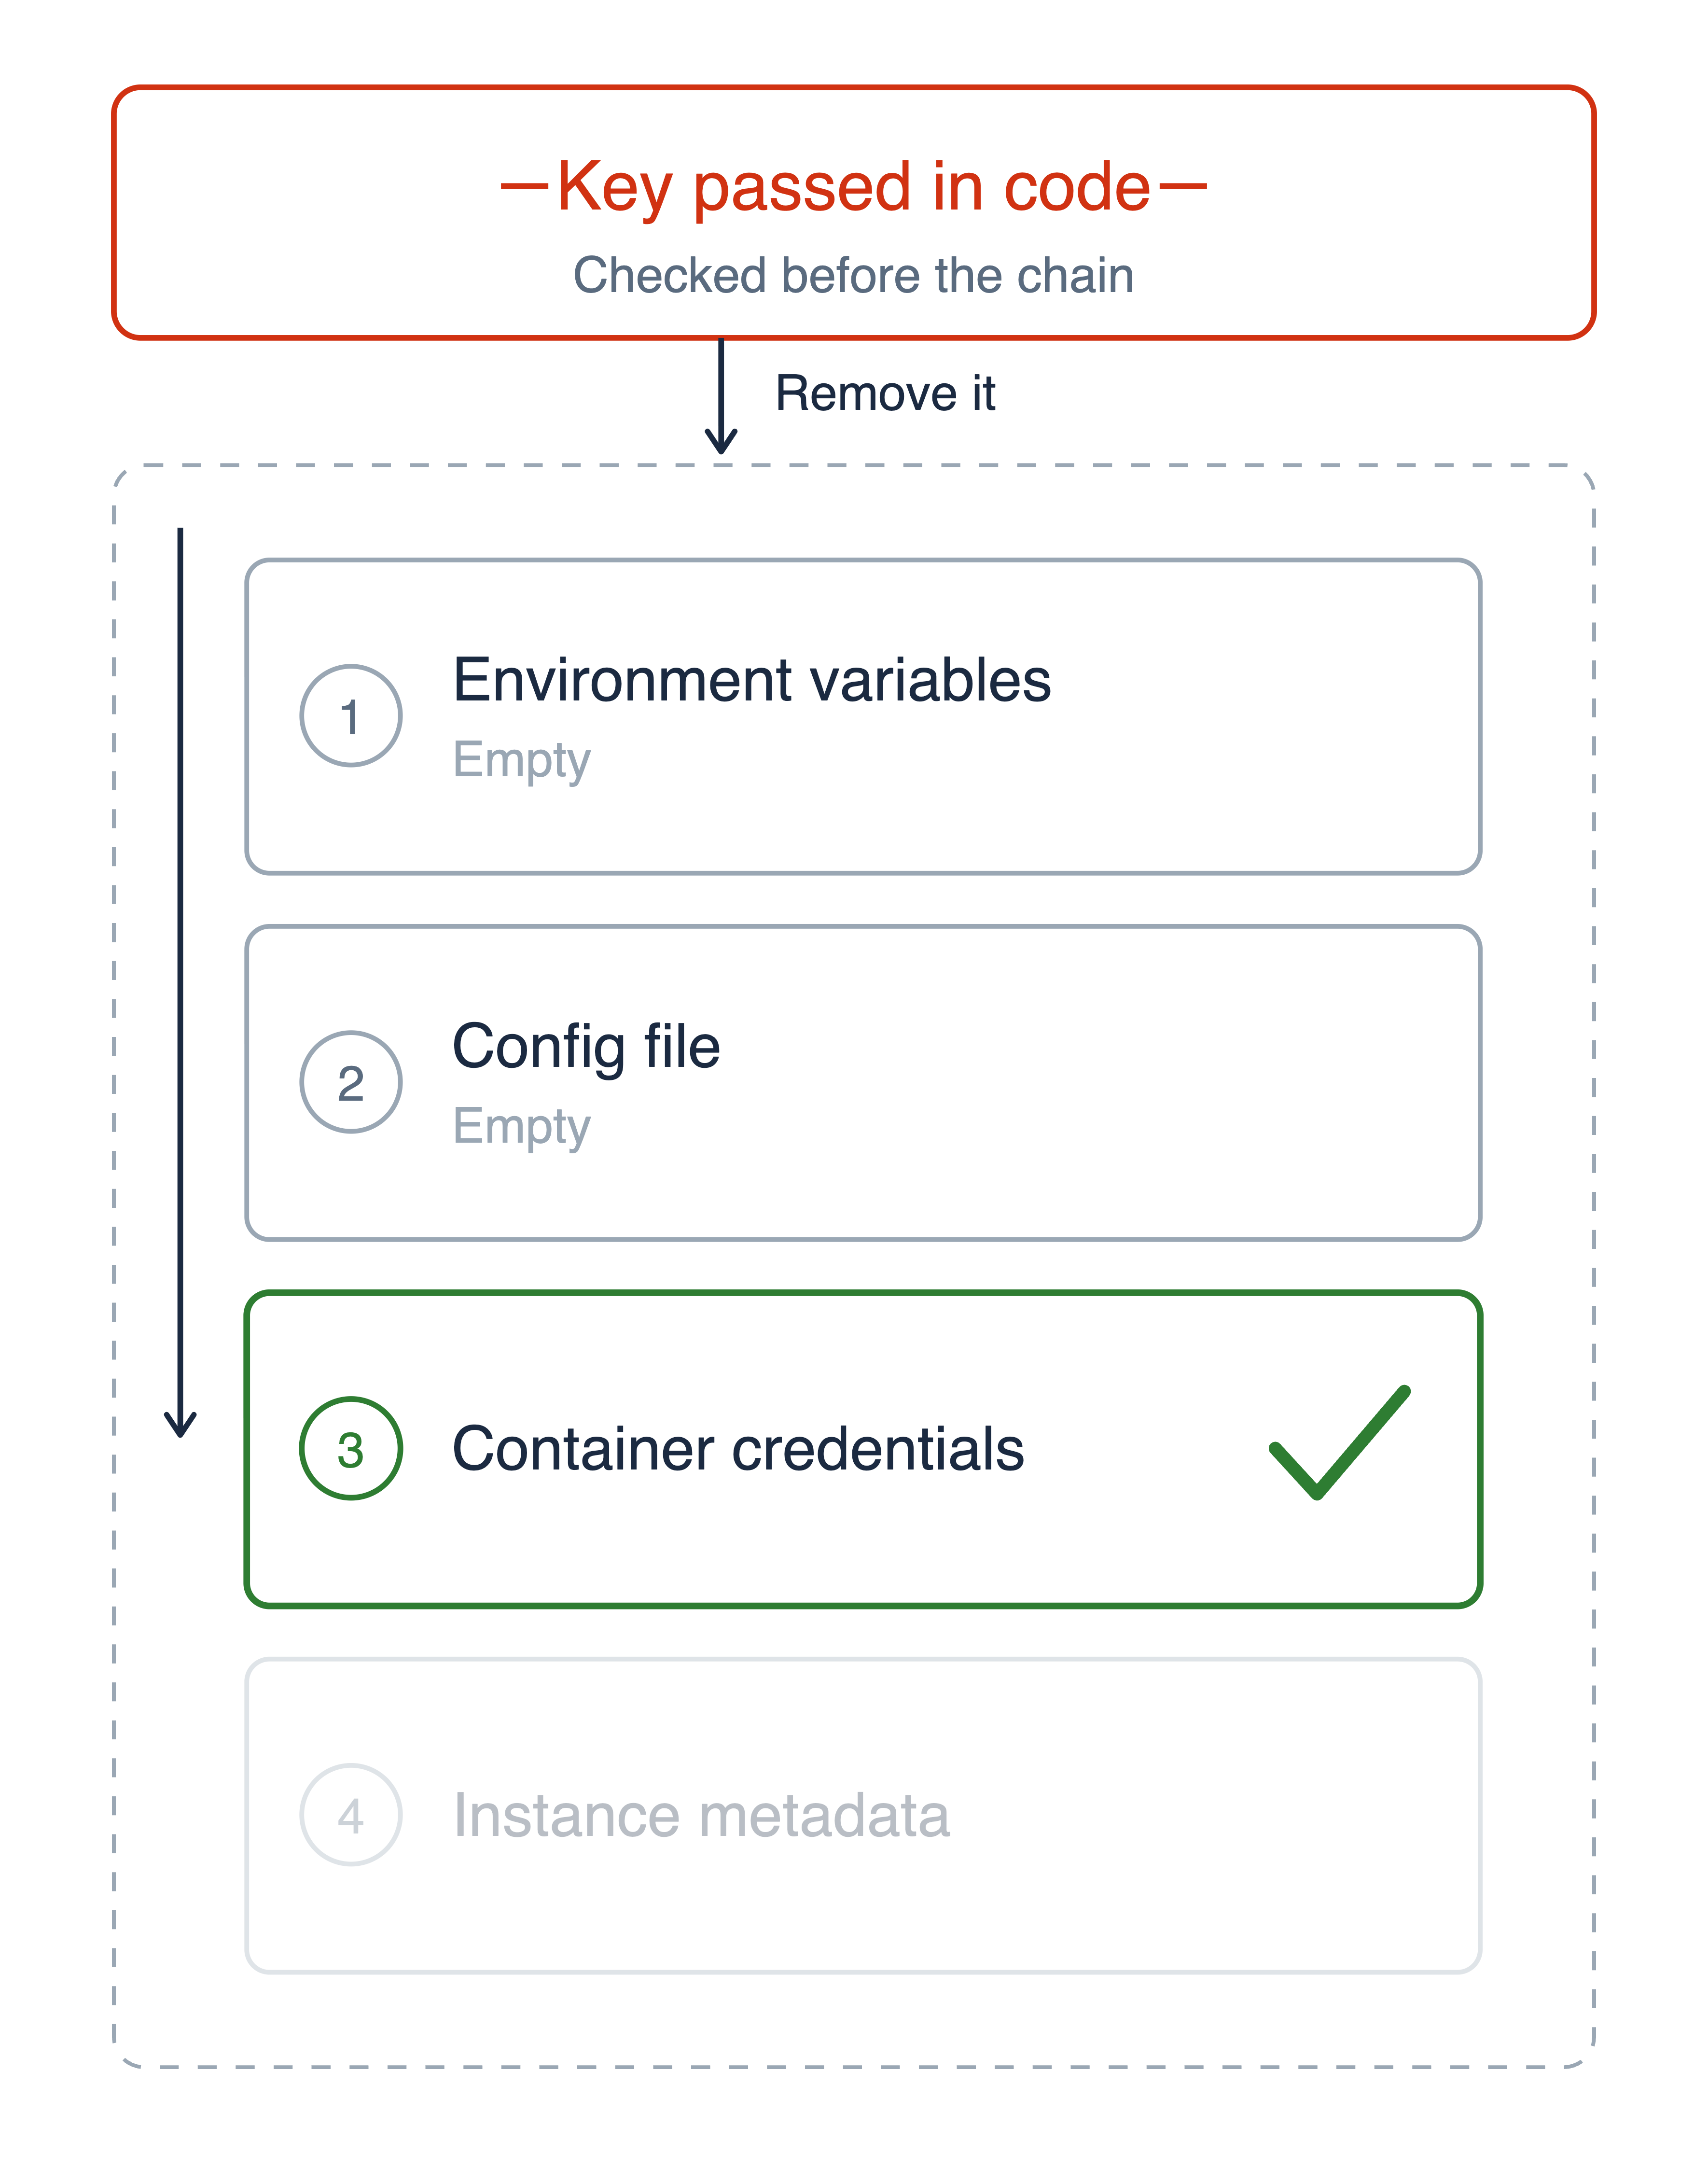
Credential provider chain जाँचना

Credential provider chain जाँचना
Hard-coded keys पहले जाँची जाती हैं, इसलिए इन्हें हटाना ज़रूरी है

1. explicit a key passed in your code
2. environment AWS_* variables, and on Lambda
that is the execution role
3. config file ~/.aws/credentials
4. container ECS or EKS task role
5. instance EC2 instance profile, via IMDS
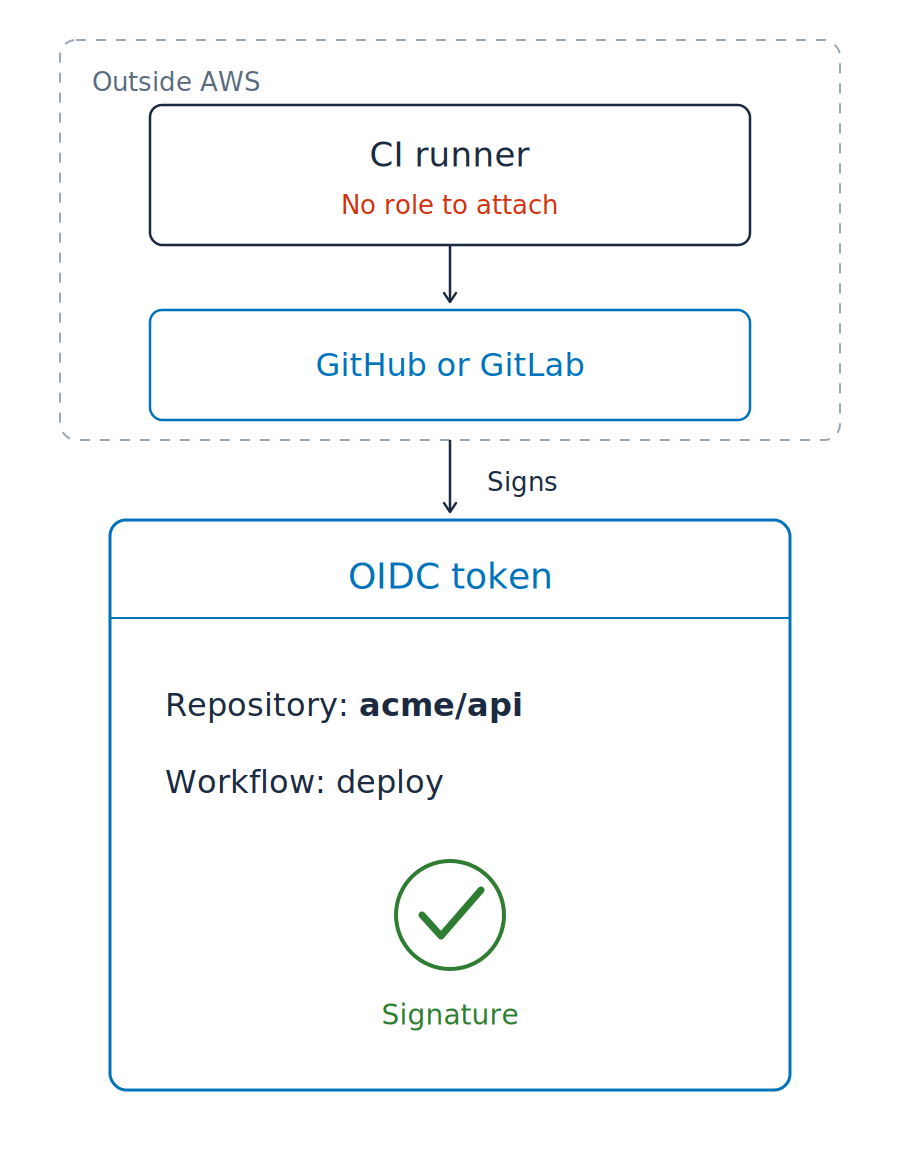
Code pipelines अक्सर AWS के बाहर चलती हैं, इसलिए credential chain जोड़ी नहीं जा सकती

Code pipelines अक्सर AWS के बाहर चलती हैं, इसलिए credential chain जोड़ी नहीं जा सकती
OIDC token (OpenID Connect)


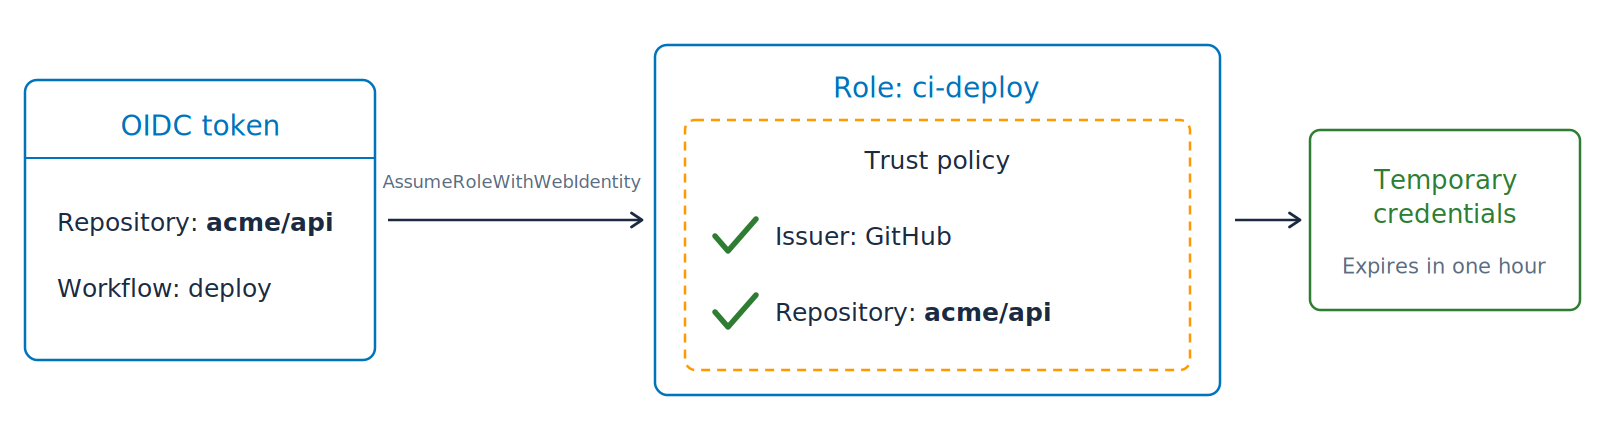
टोकन को credentials में बदलना

टोकन को credentials में बदलना
Repository secrets: अब खाली
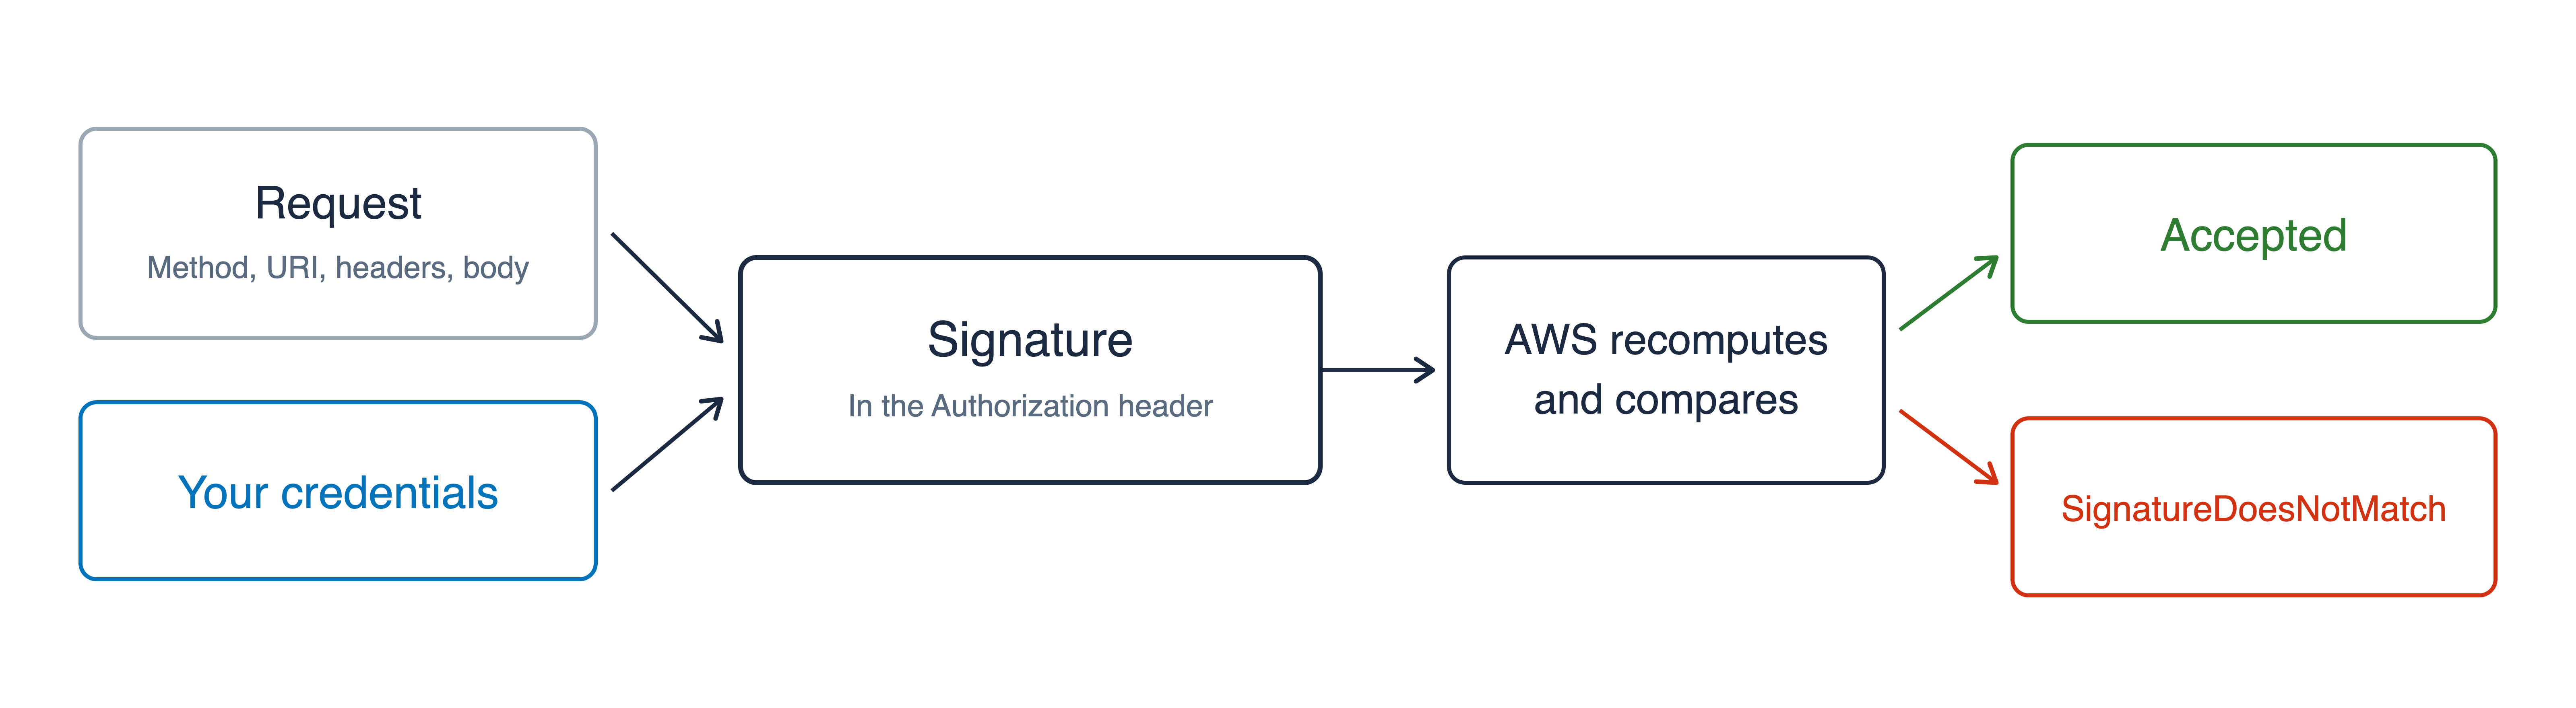
Signature Version 4, या SigV4

अस्थायी credentials

अस्थायी credentials
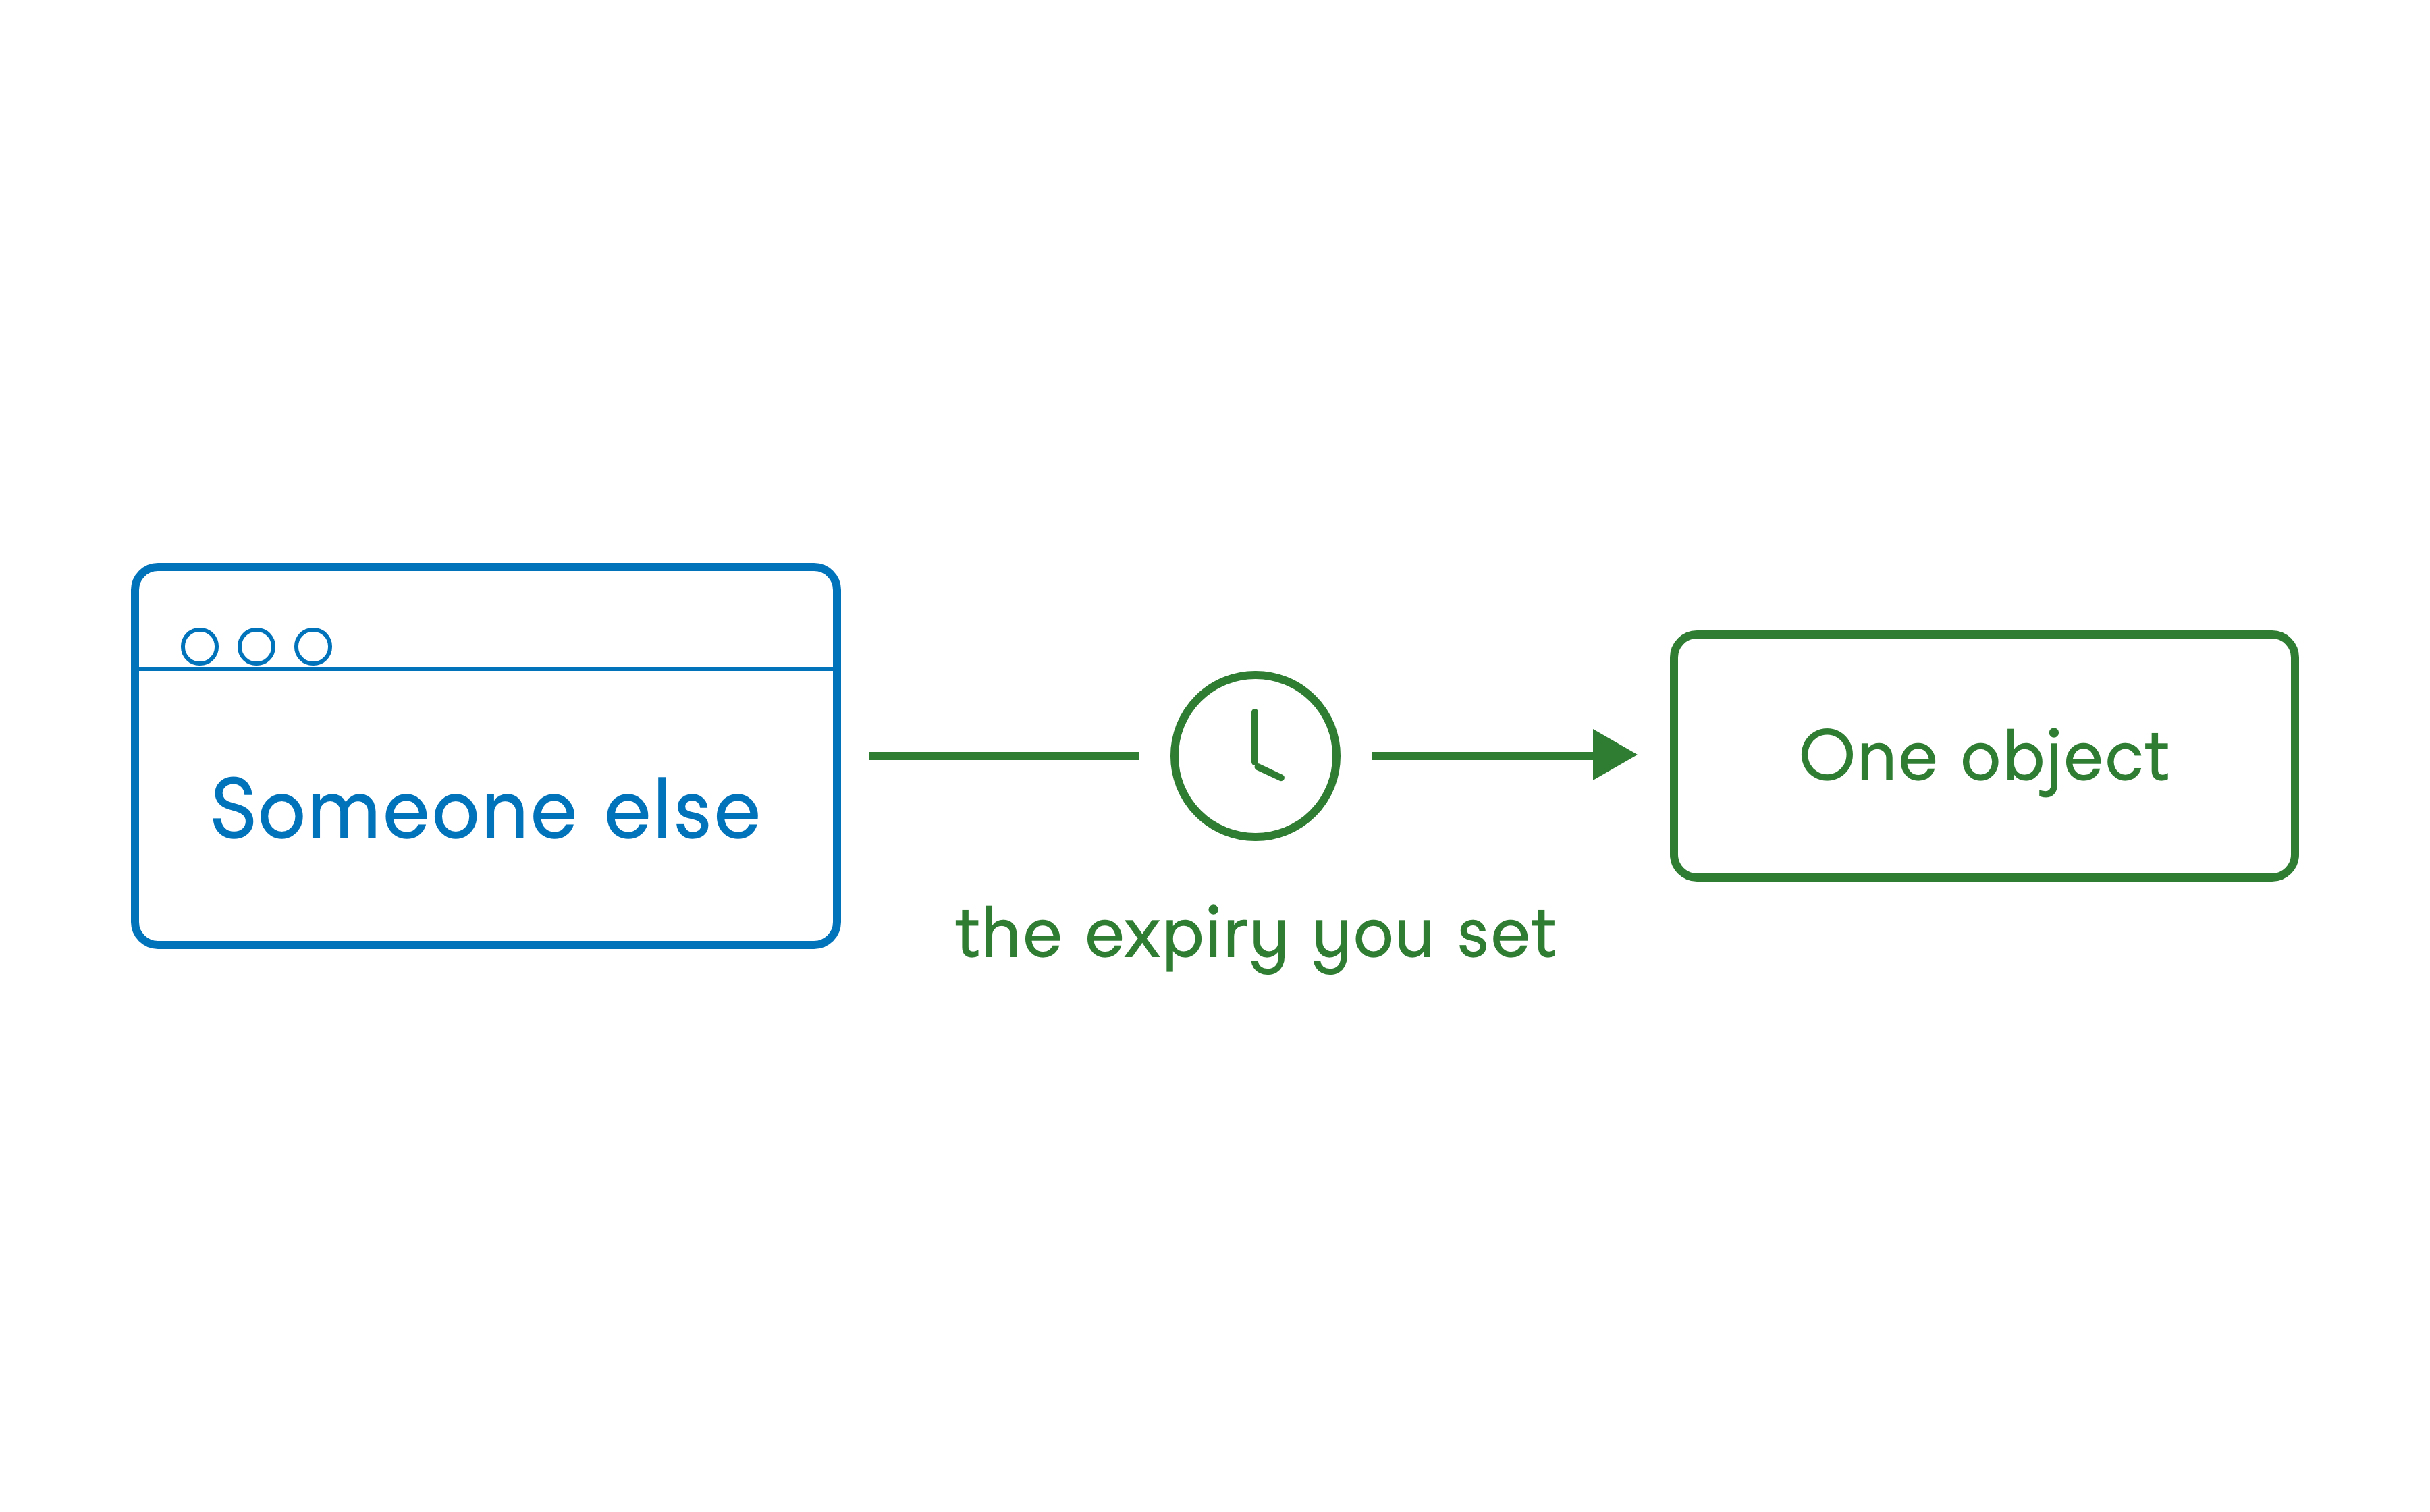
Pre-signed URL


डेवलपर्स के लिए AWS Security का उपयोग