การใช้ AWS Security สำหรับนักพัฒนา
Rahul Singh
Technical Product Manager
{
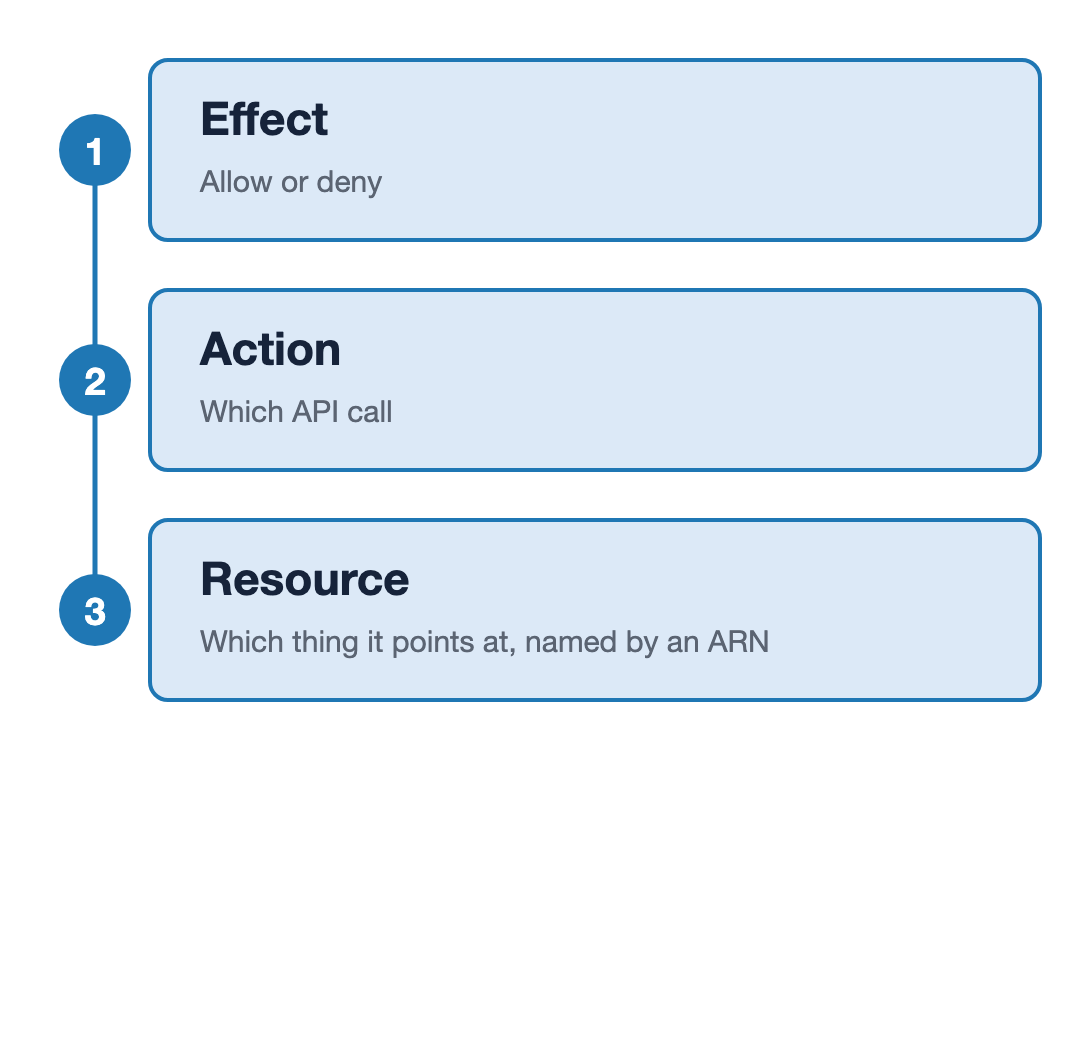
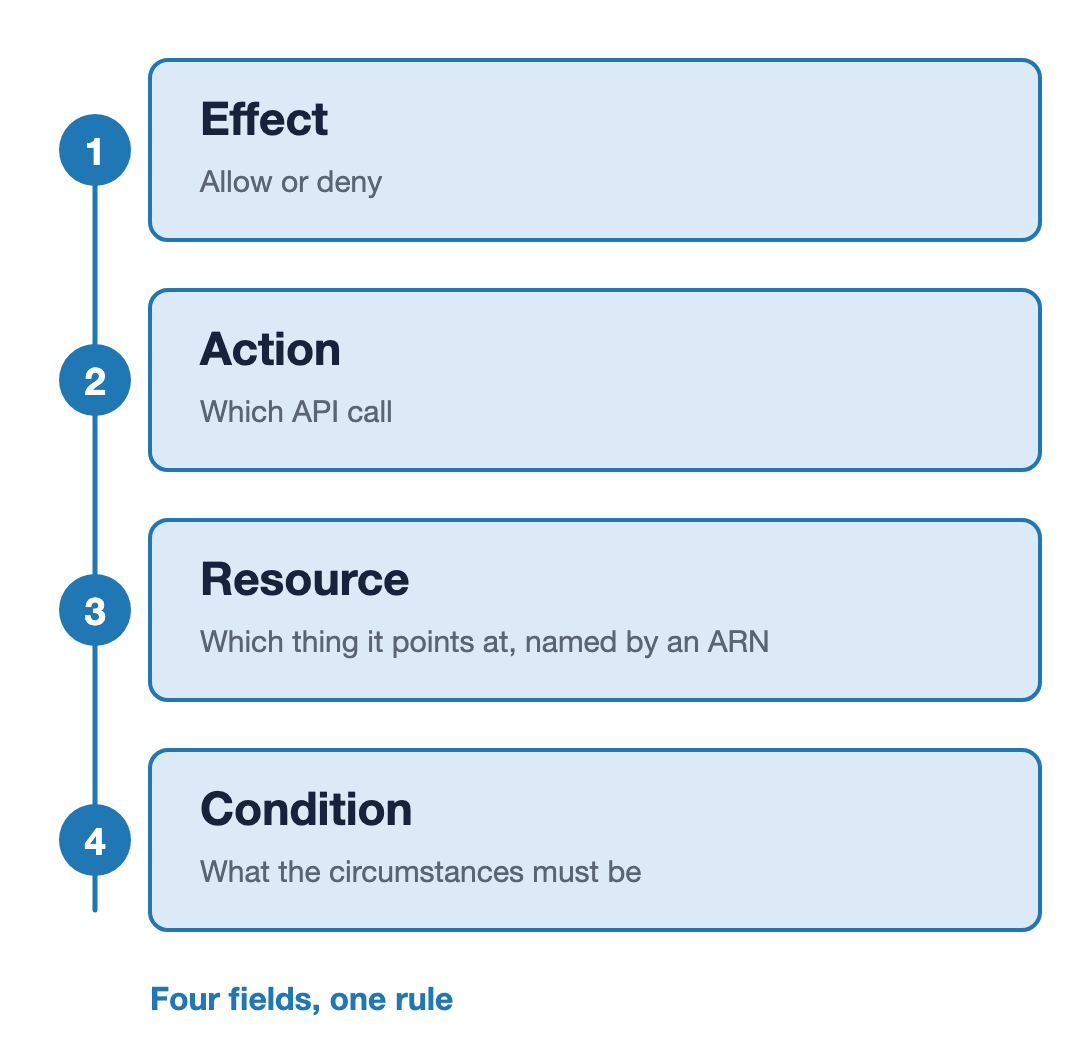
"Effect": "Allow",
"Action": "s3:GetObject",
"Resource": "arn:aws:s3:::reports/*",
"Condition": {
"Bool": {
"aws:SecureTransport": "true"
},
"IpAddress": {
"aws:SourceIp": "203.0.113.0/24"
}
}
}

{
"Effect": "Allow",
"Action": "s3:GetObject",
"Resource": "arn:aws:s3:::reports/*",
"Condition": {
"Bool": {
"aws:SecureTransport": "true"
},
"IpAddress": {
"aws:SourceIp": "203.0.113.0/24"
}
}
}

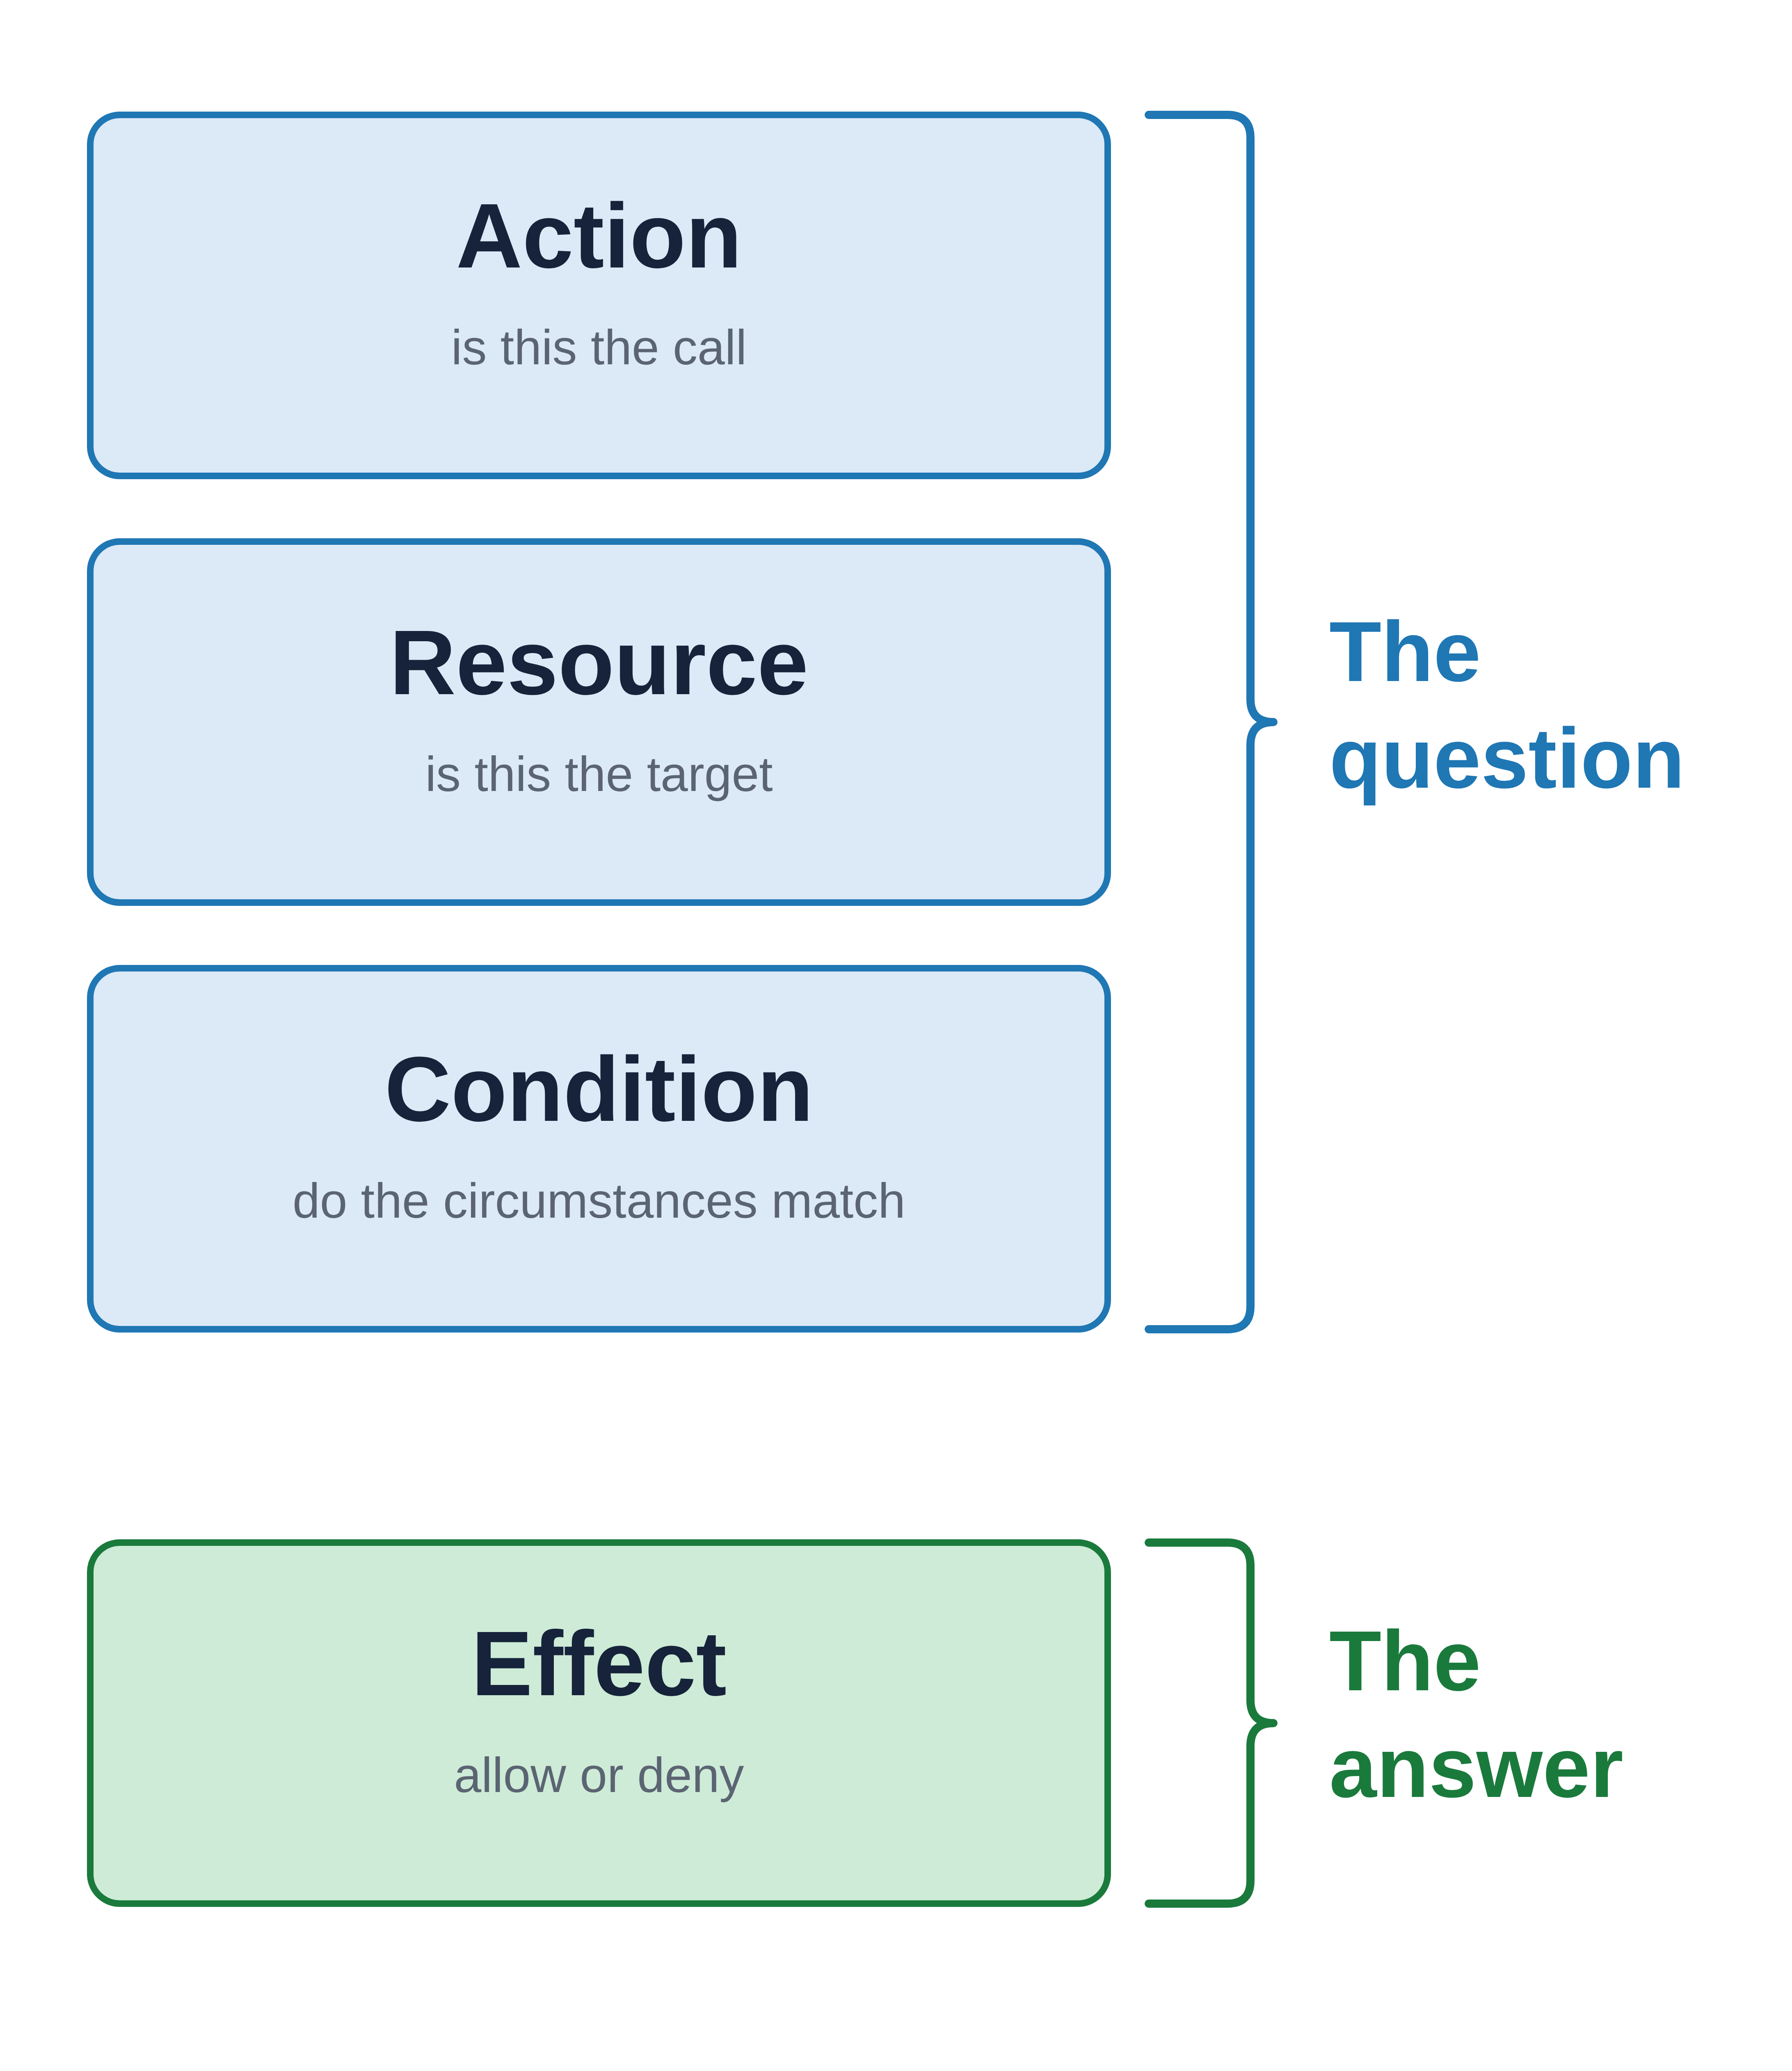
คำถาม
คำตอบ


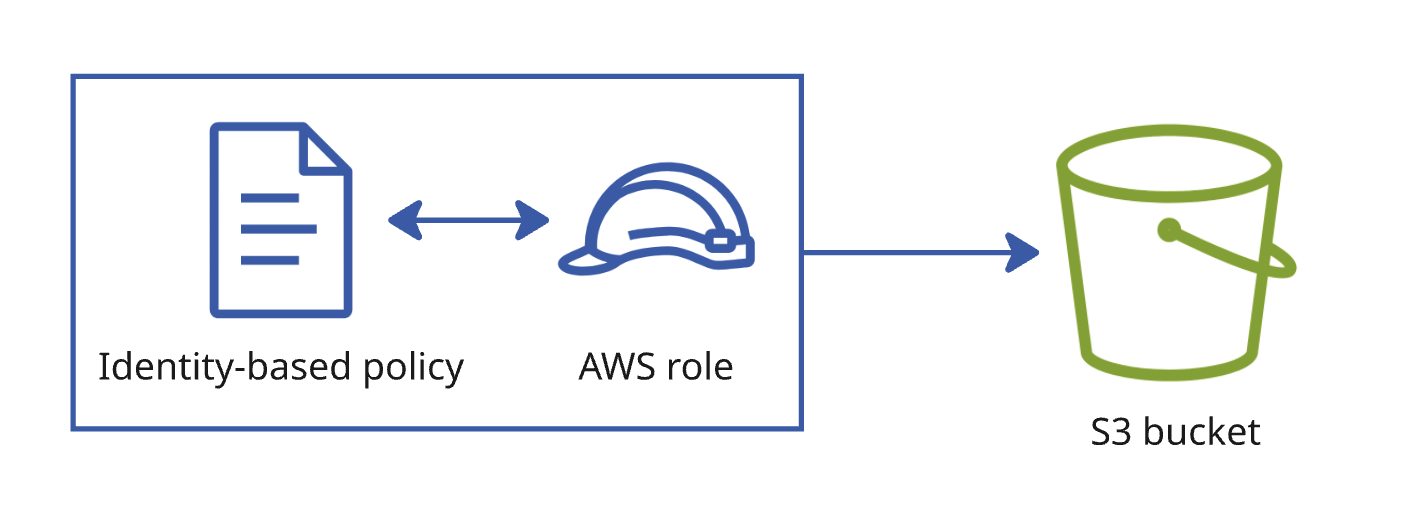
Identity-based


Identity-based
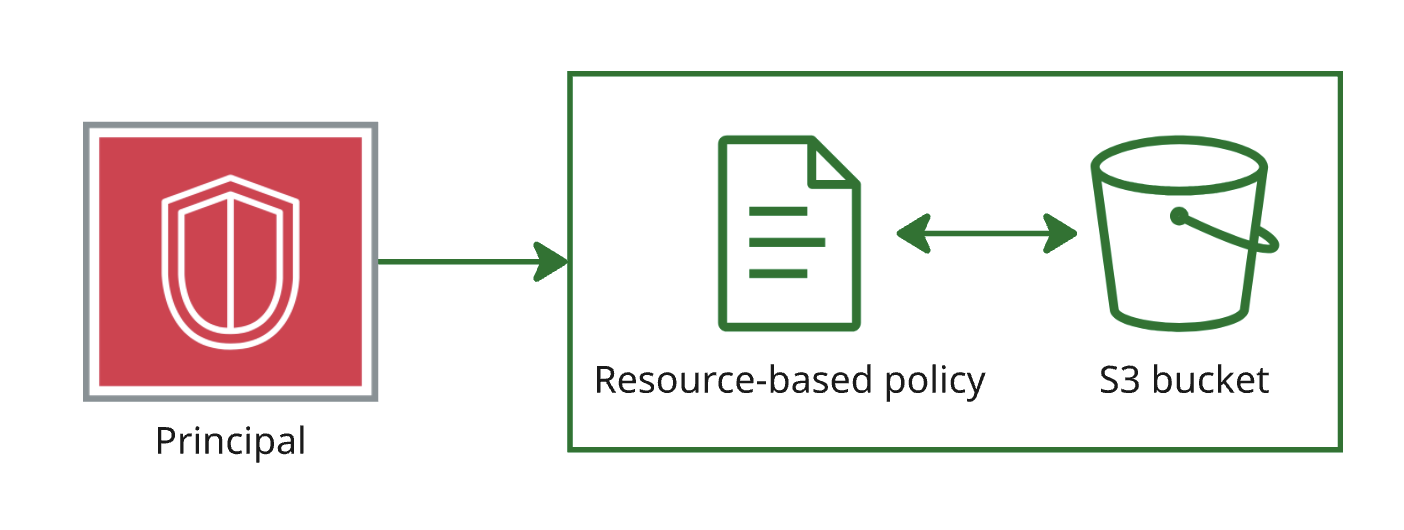
Resource-based
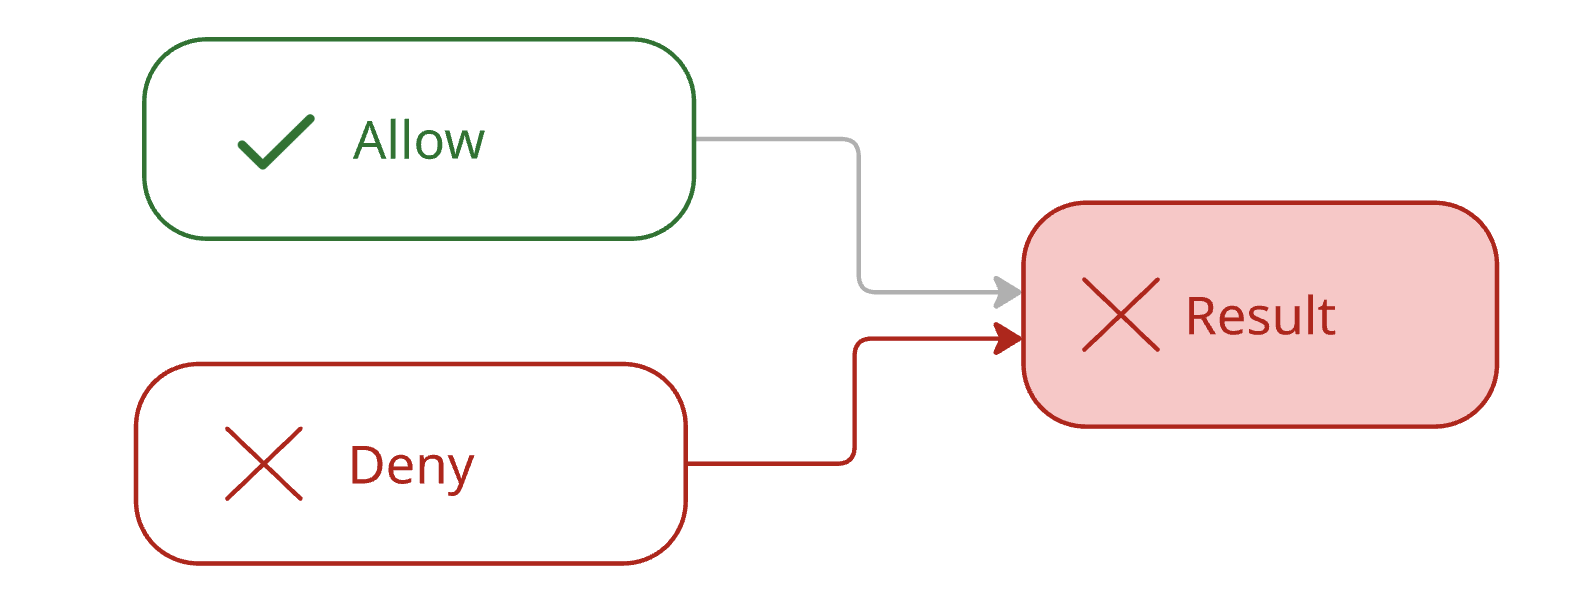
{"Effect": "Allow", "Action": "s3:*", "Resource": "*"}
{"Effect": "Deny", "Action": "s3:DeleteObject", "Resource": "*"}
{"Effect": "Allow", "Action": "s3:*", "Resource": "*"}
{"Effect": "Deny", "Action": "s3:DeleteObject", "Resource": "*"}
คำขอ: s3:DeleteObject ส่งผลให้: ถูกปฏิเสธ
การปฏิเสธแบบชัดเจนชนะ allow ใดๆ ไม่ว่าจะกว้างแค่ไหน


{"Effect": "Allow", "Action": "s3:*",
"Resource": "*"}
{"Effect": "Deny", "Action": "s3:DeleteObject",
"Resource": "*"}
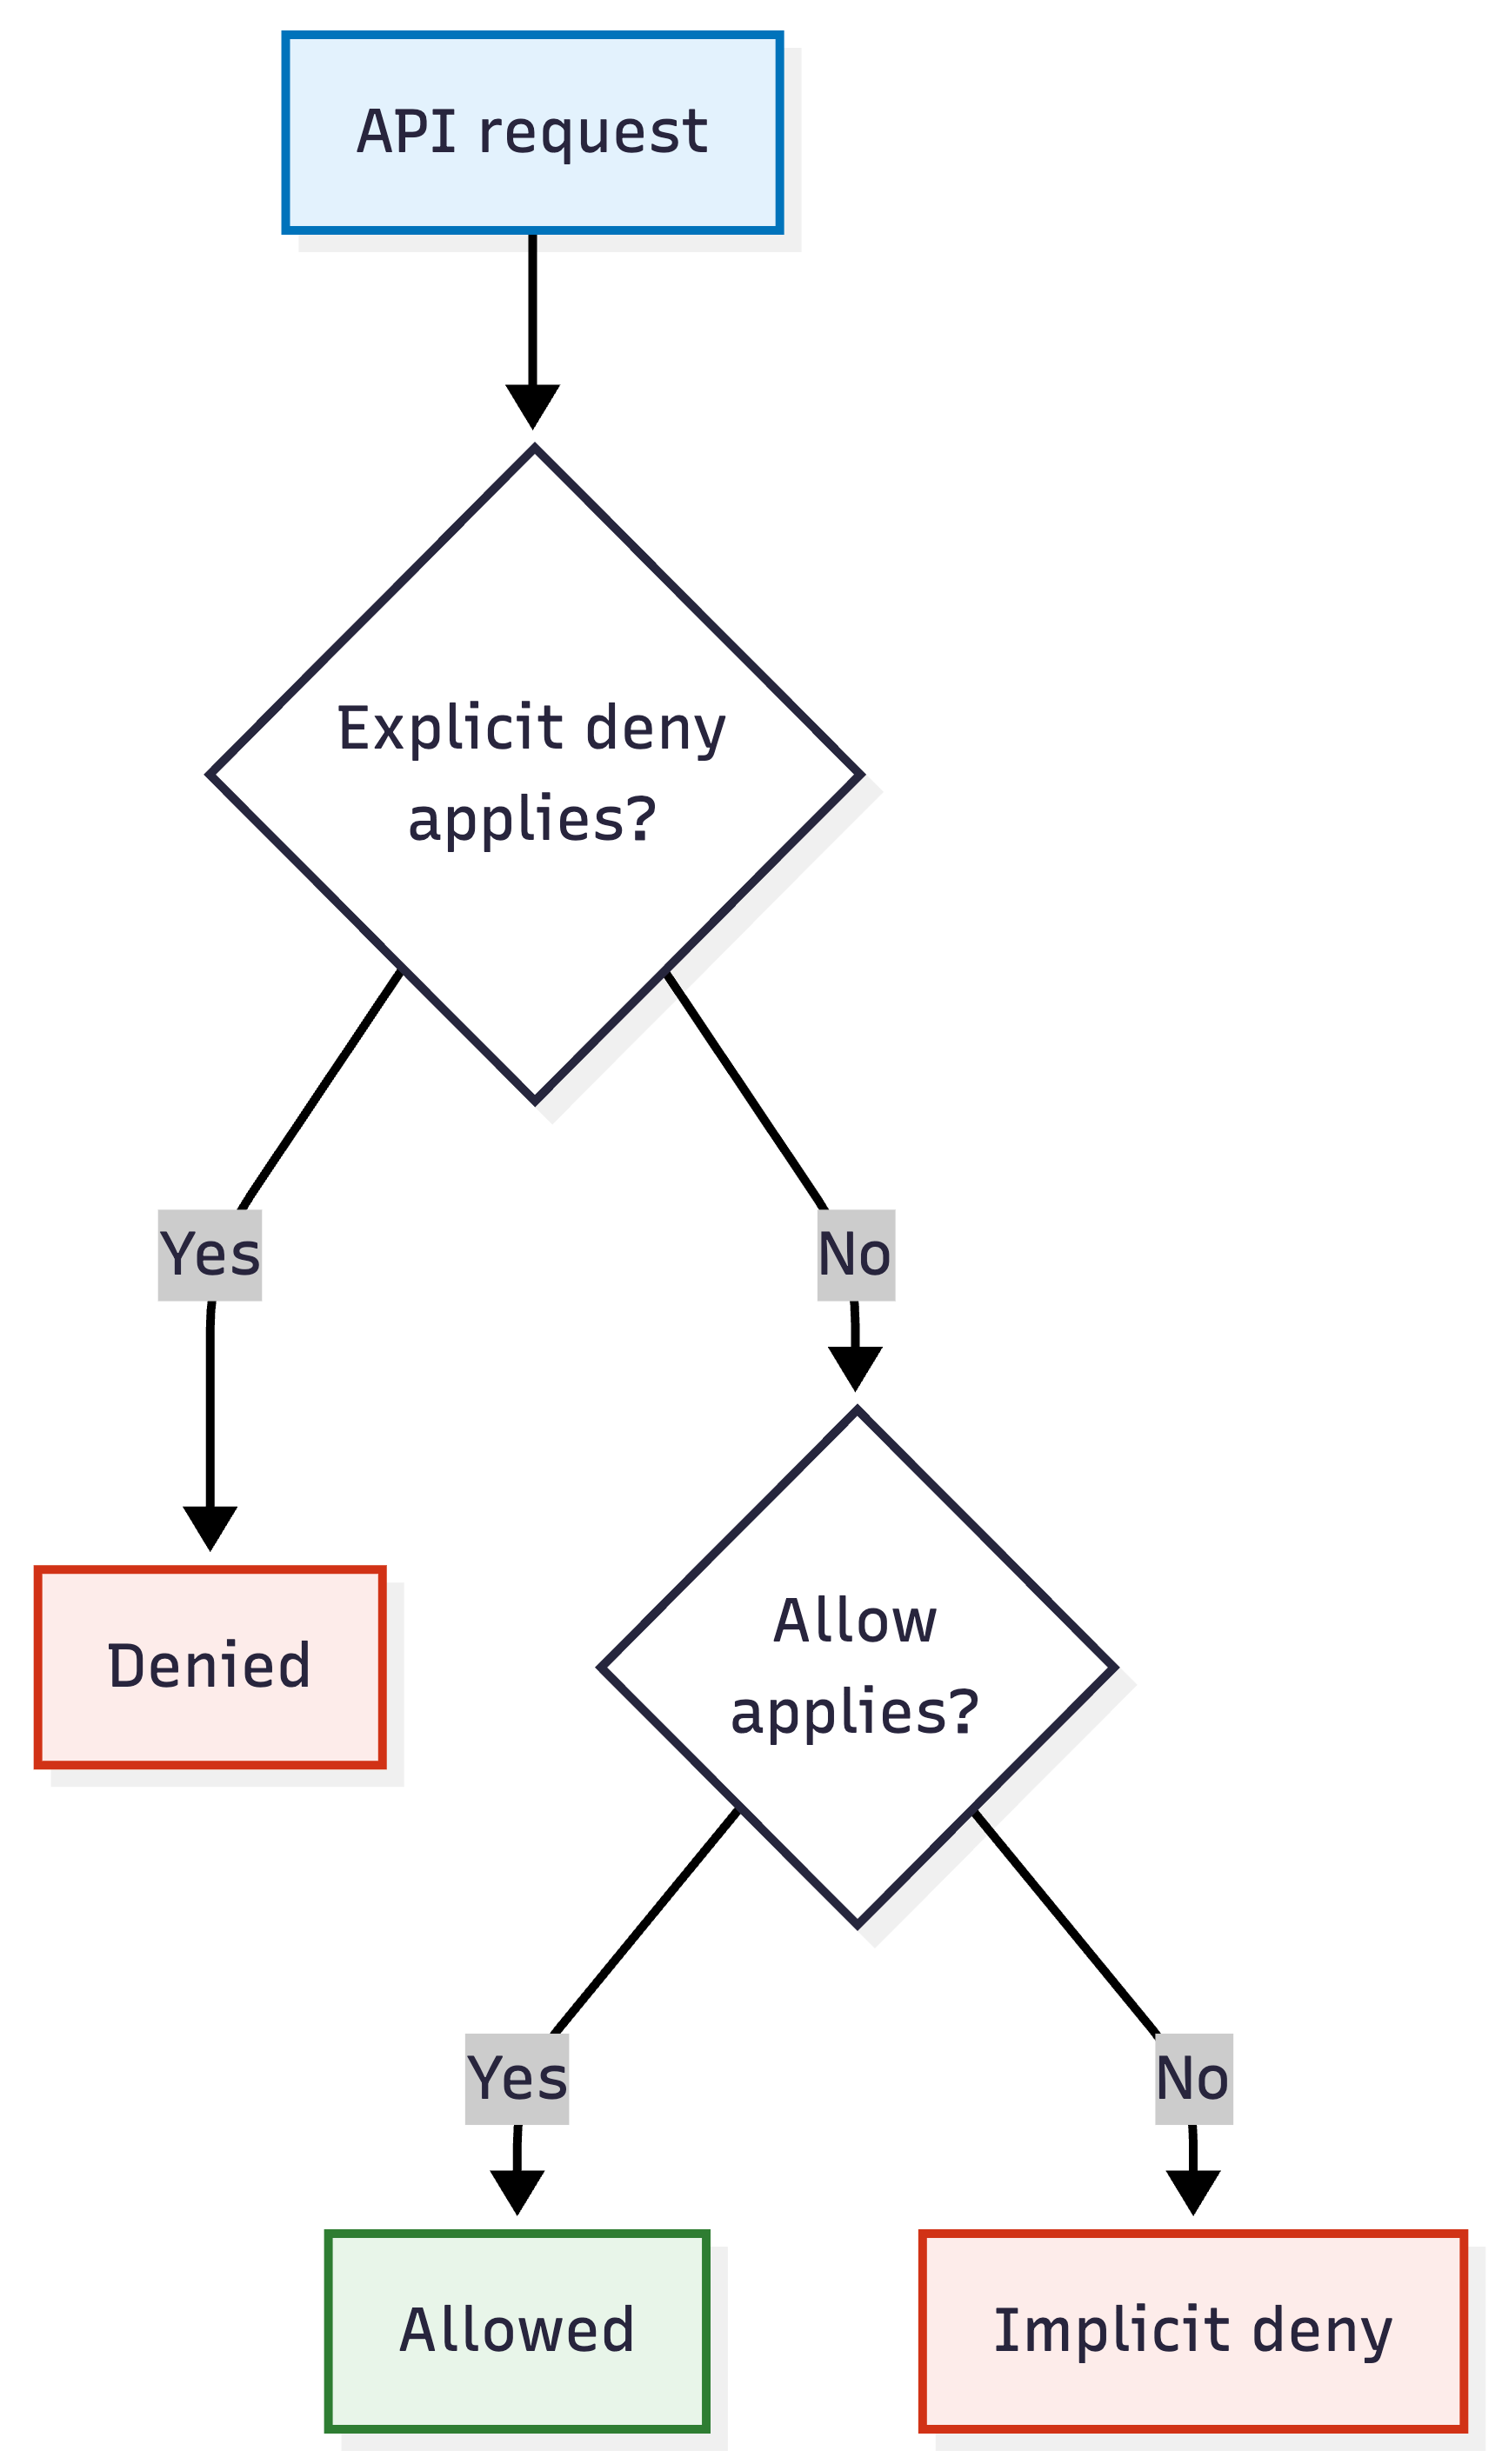
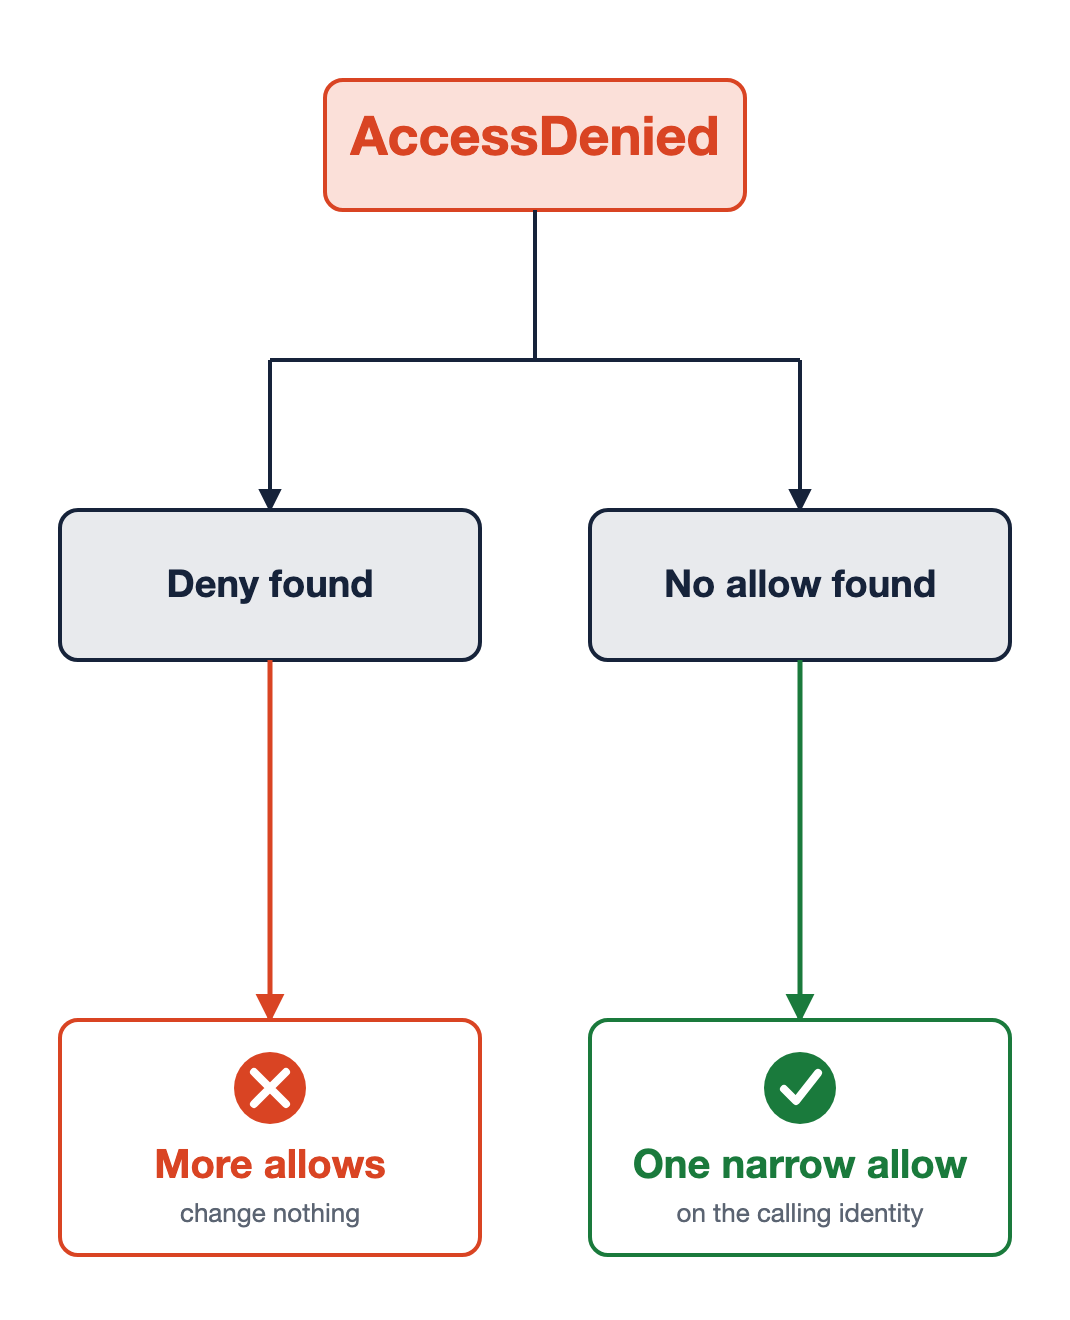
s3:GetObject → allow: allow ที่ครอบคลุมกว้างครอบคลุมถึงs3:DeleteObject → explicit deny: มีคำสั่งบอกว่าไม่kms:Decrypt, dynamodb:GetItem → implicit deny: นโยบายนี้ไม่เคยกล่าวถึงบริการเหล่านั้นข้อผิดพลาดเดียวกัน สองสาเหตุ
การปฏิเสธแบบชัดเจน
การปฏิเสธแบบนัย

การใช้ AWS Security สำหรับนักพัฒนา